Signed decisions
Approving a device, or marking it not approved, is a decision signed with your name and an authenticator code, and recorded in the audit log.
Decide · Weekly review
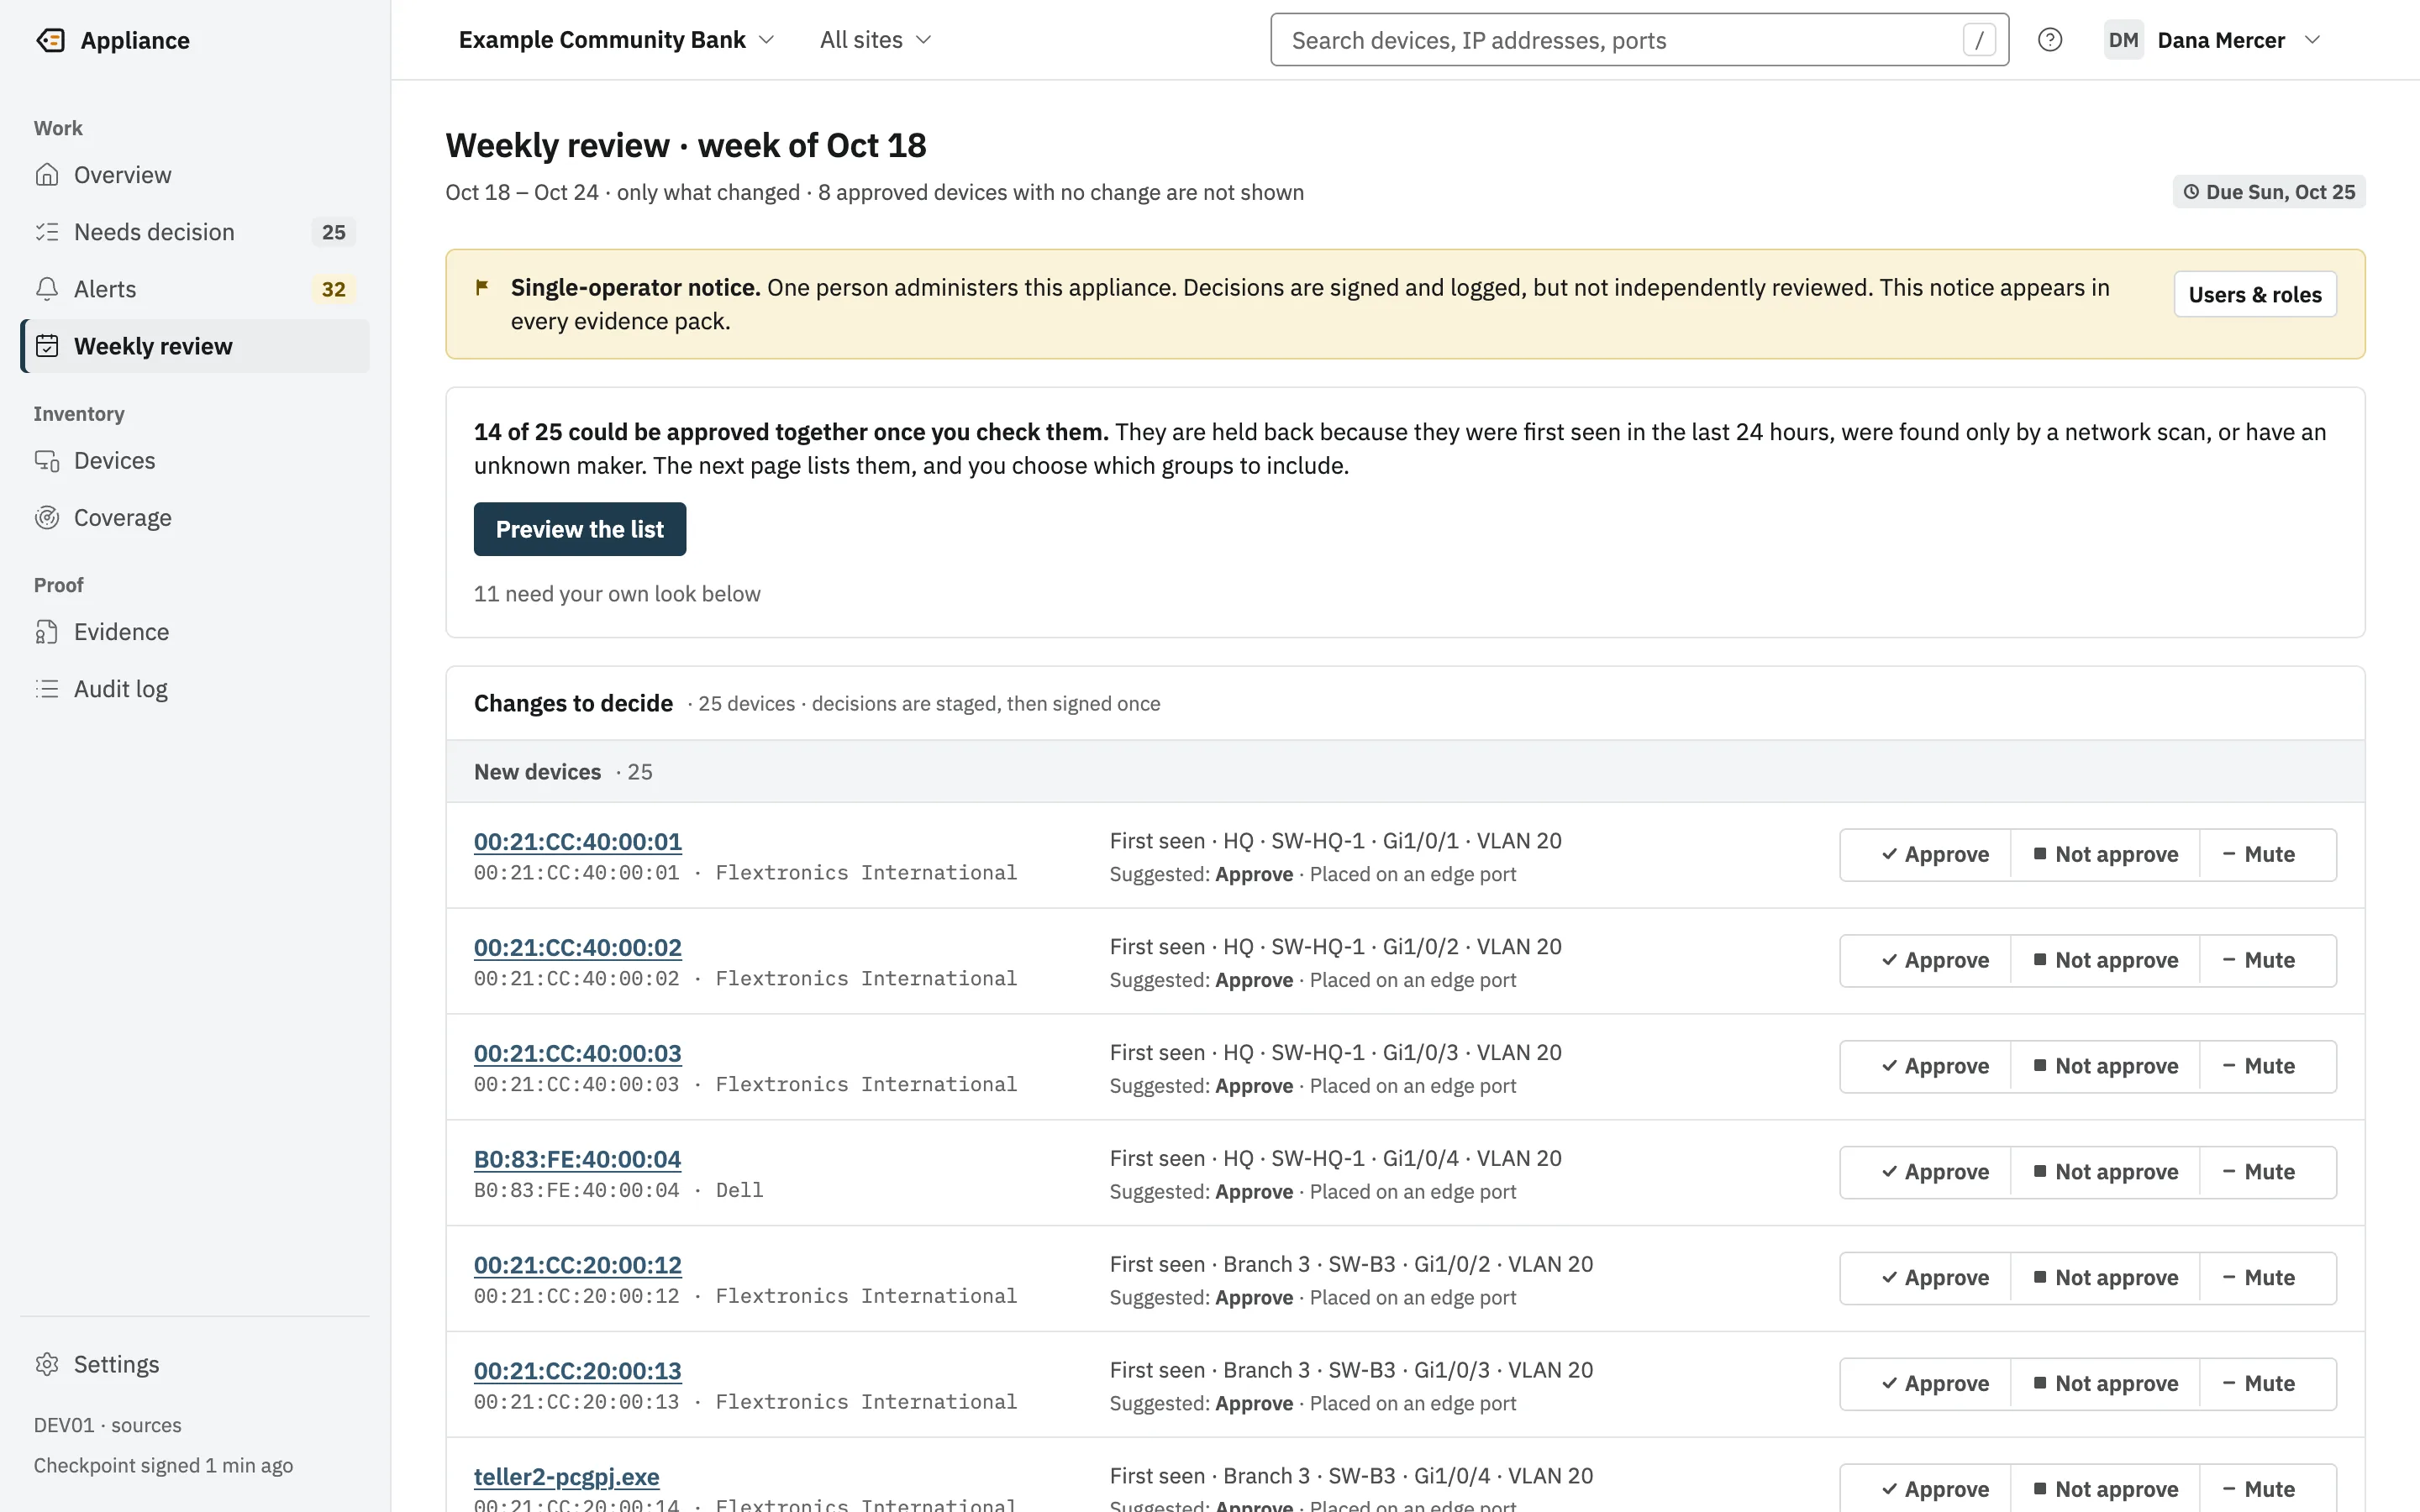
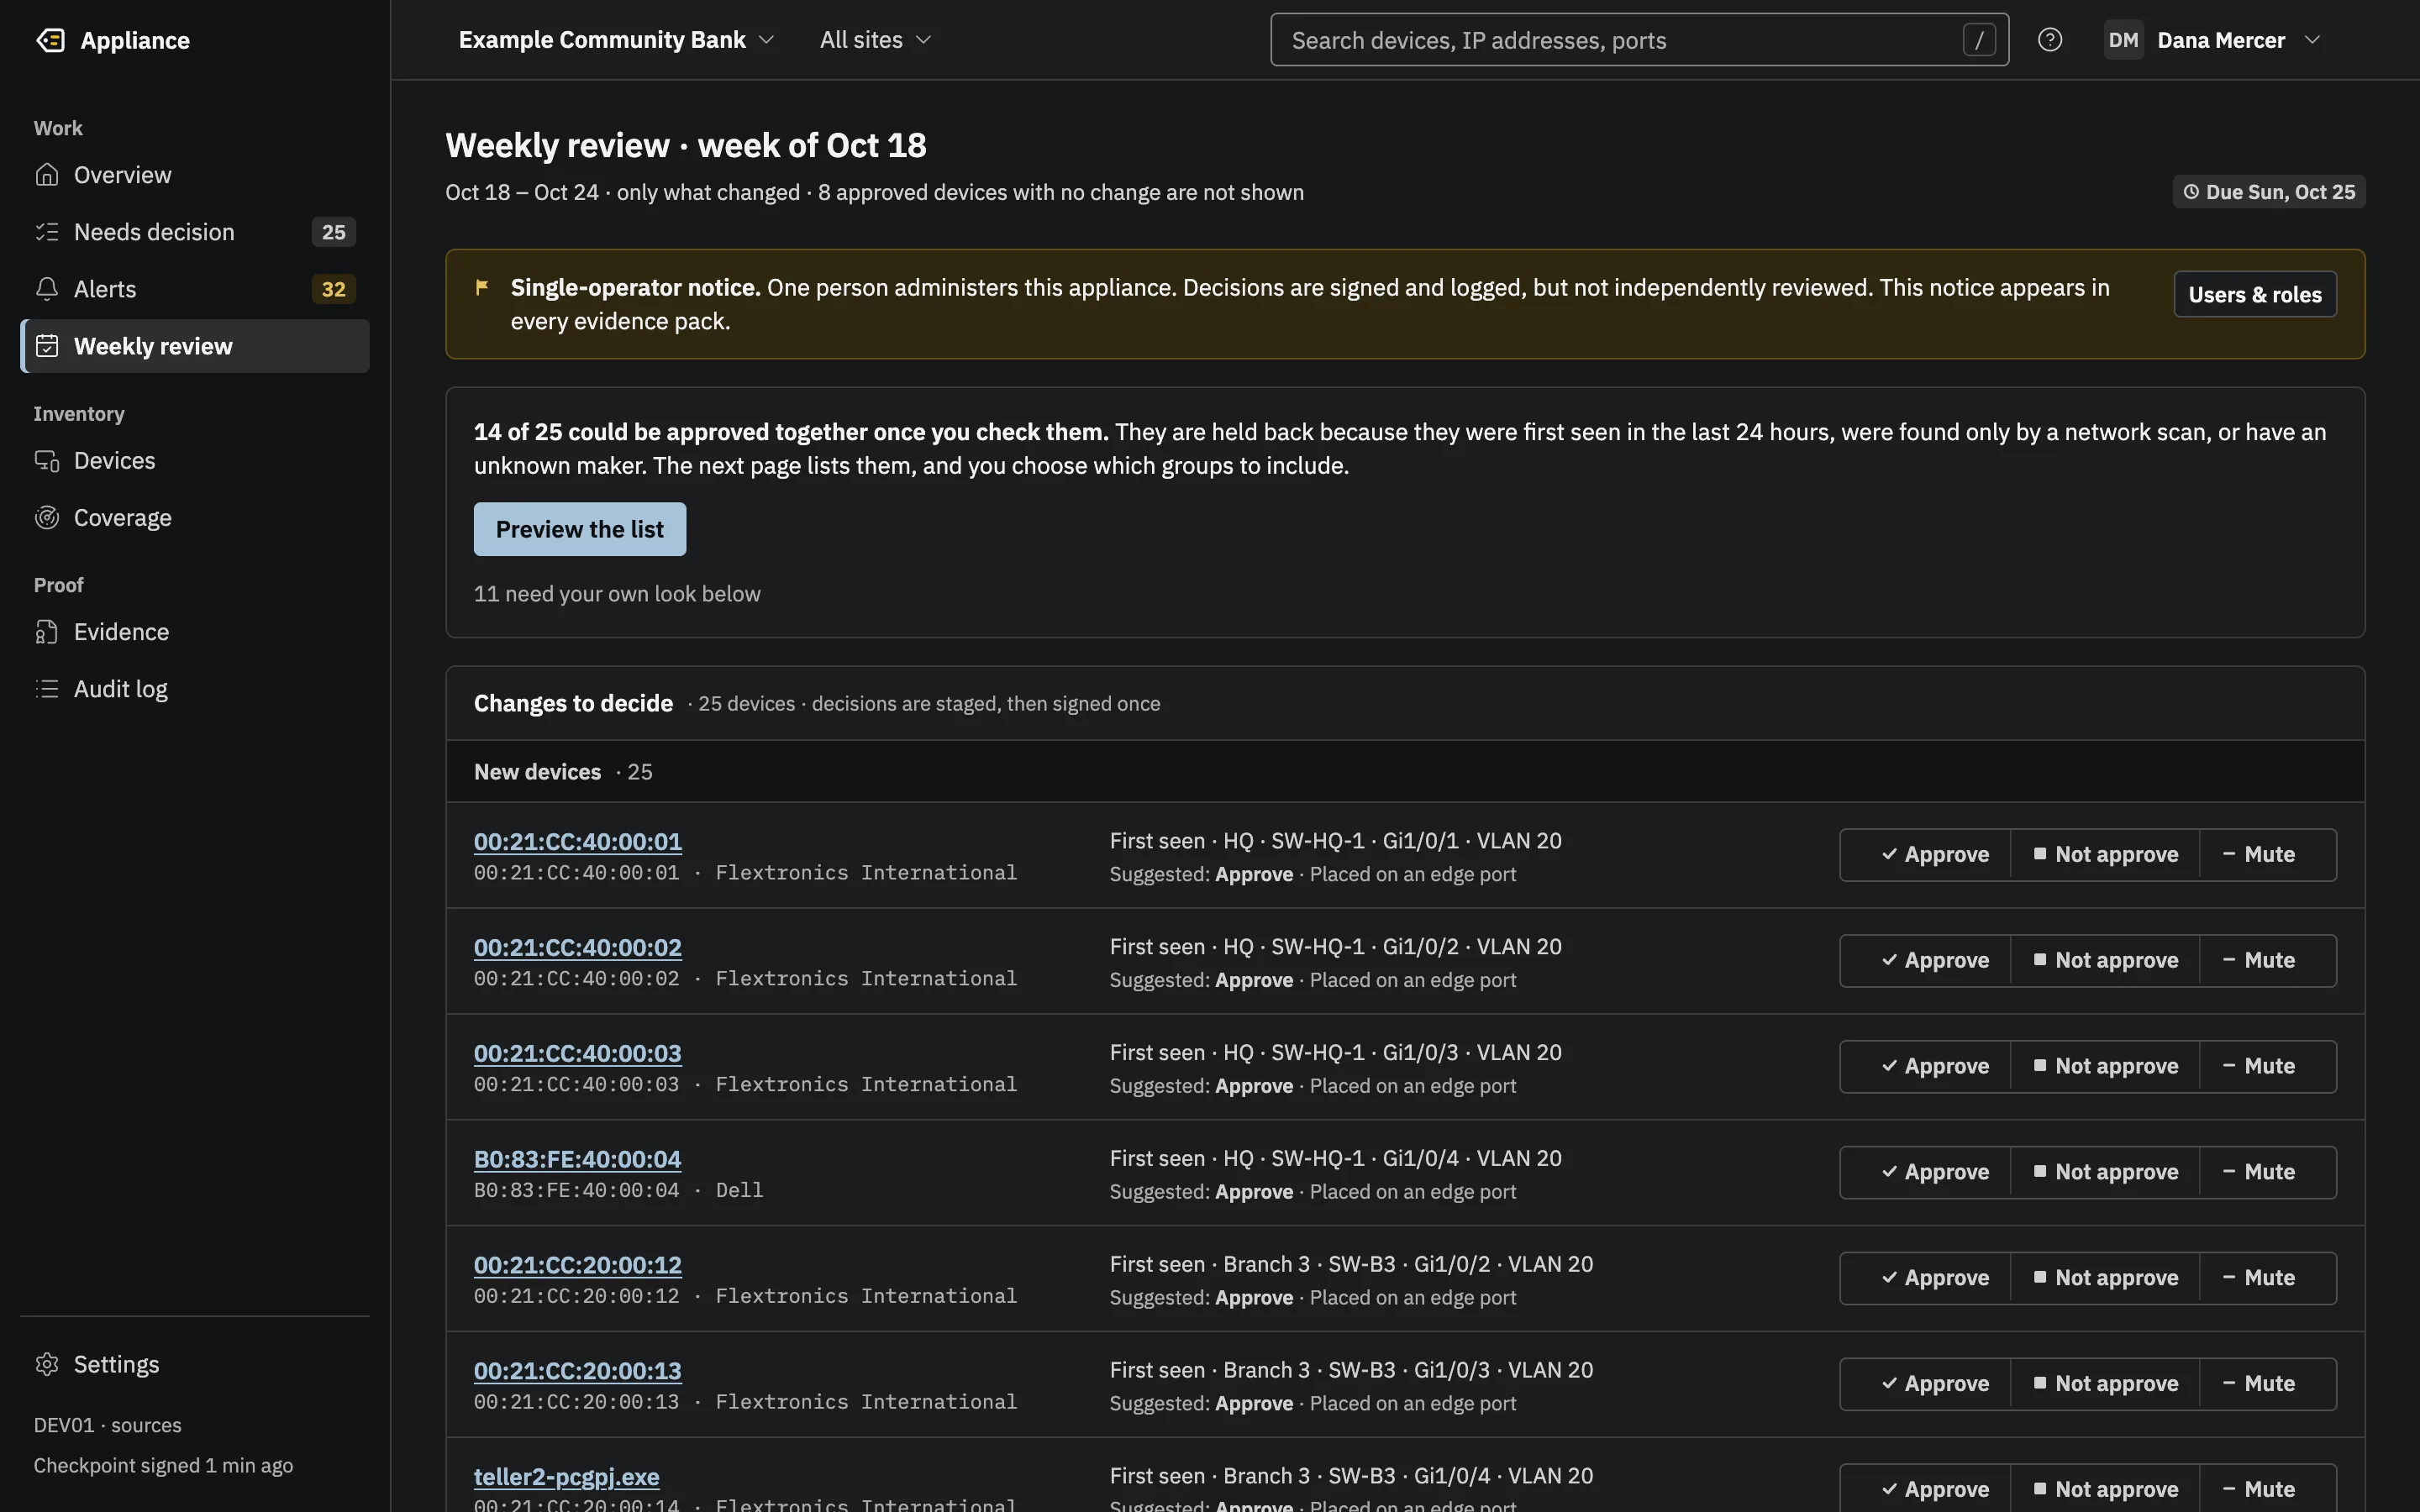
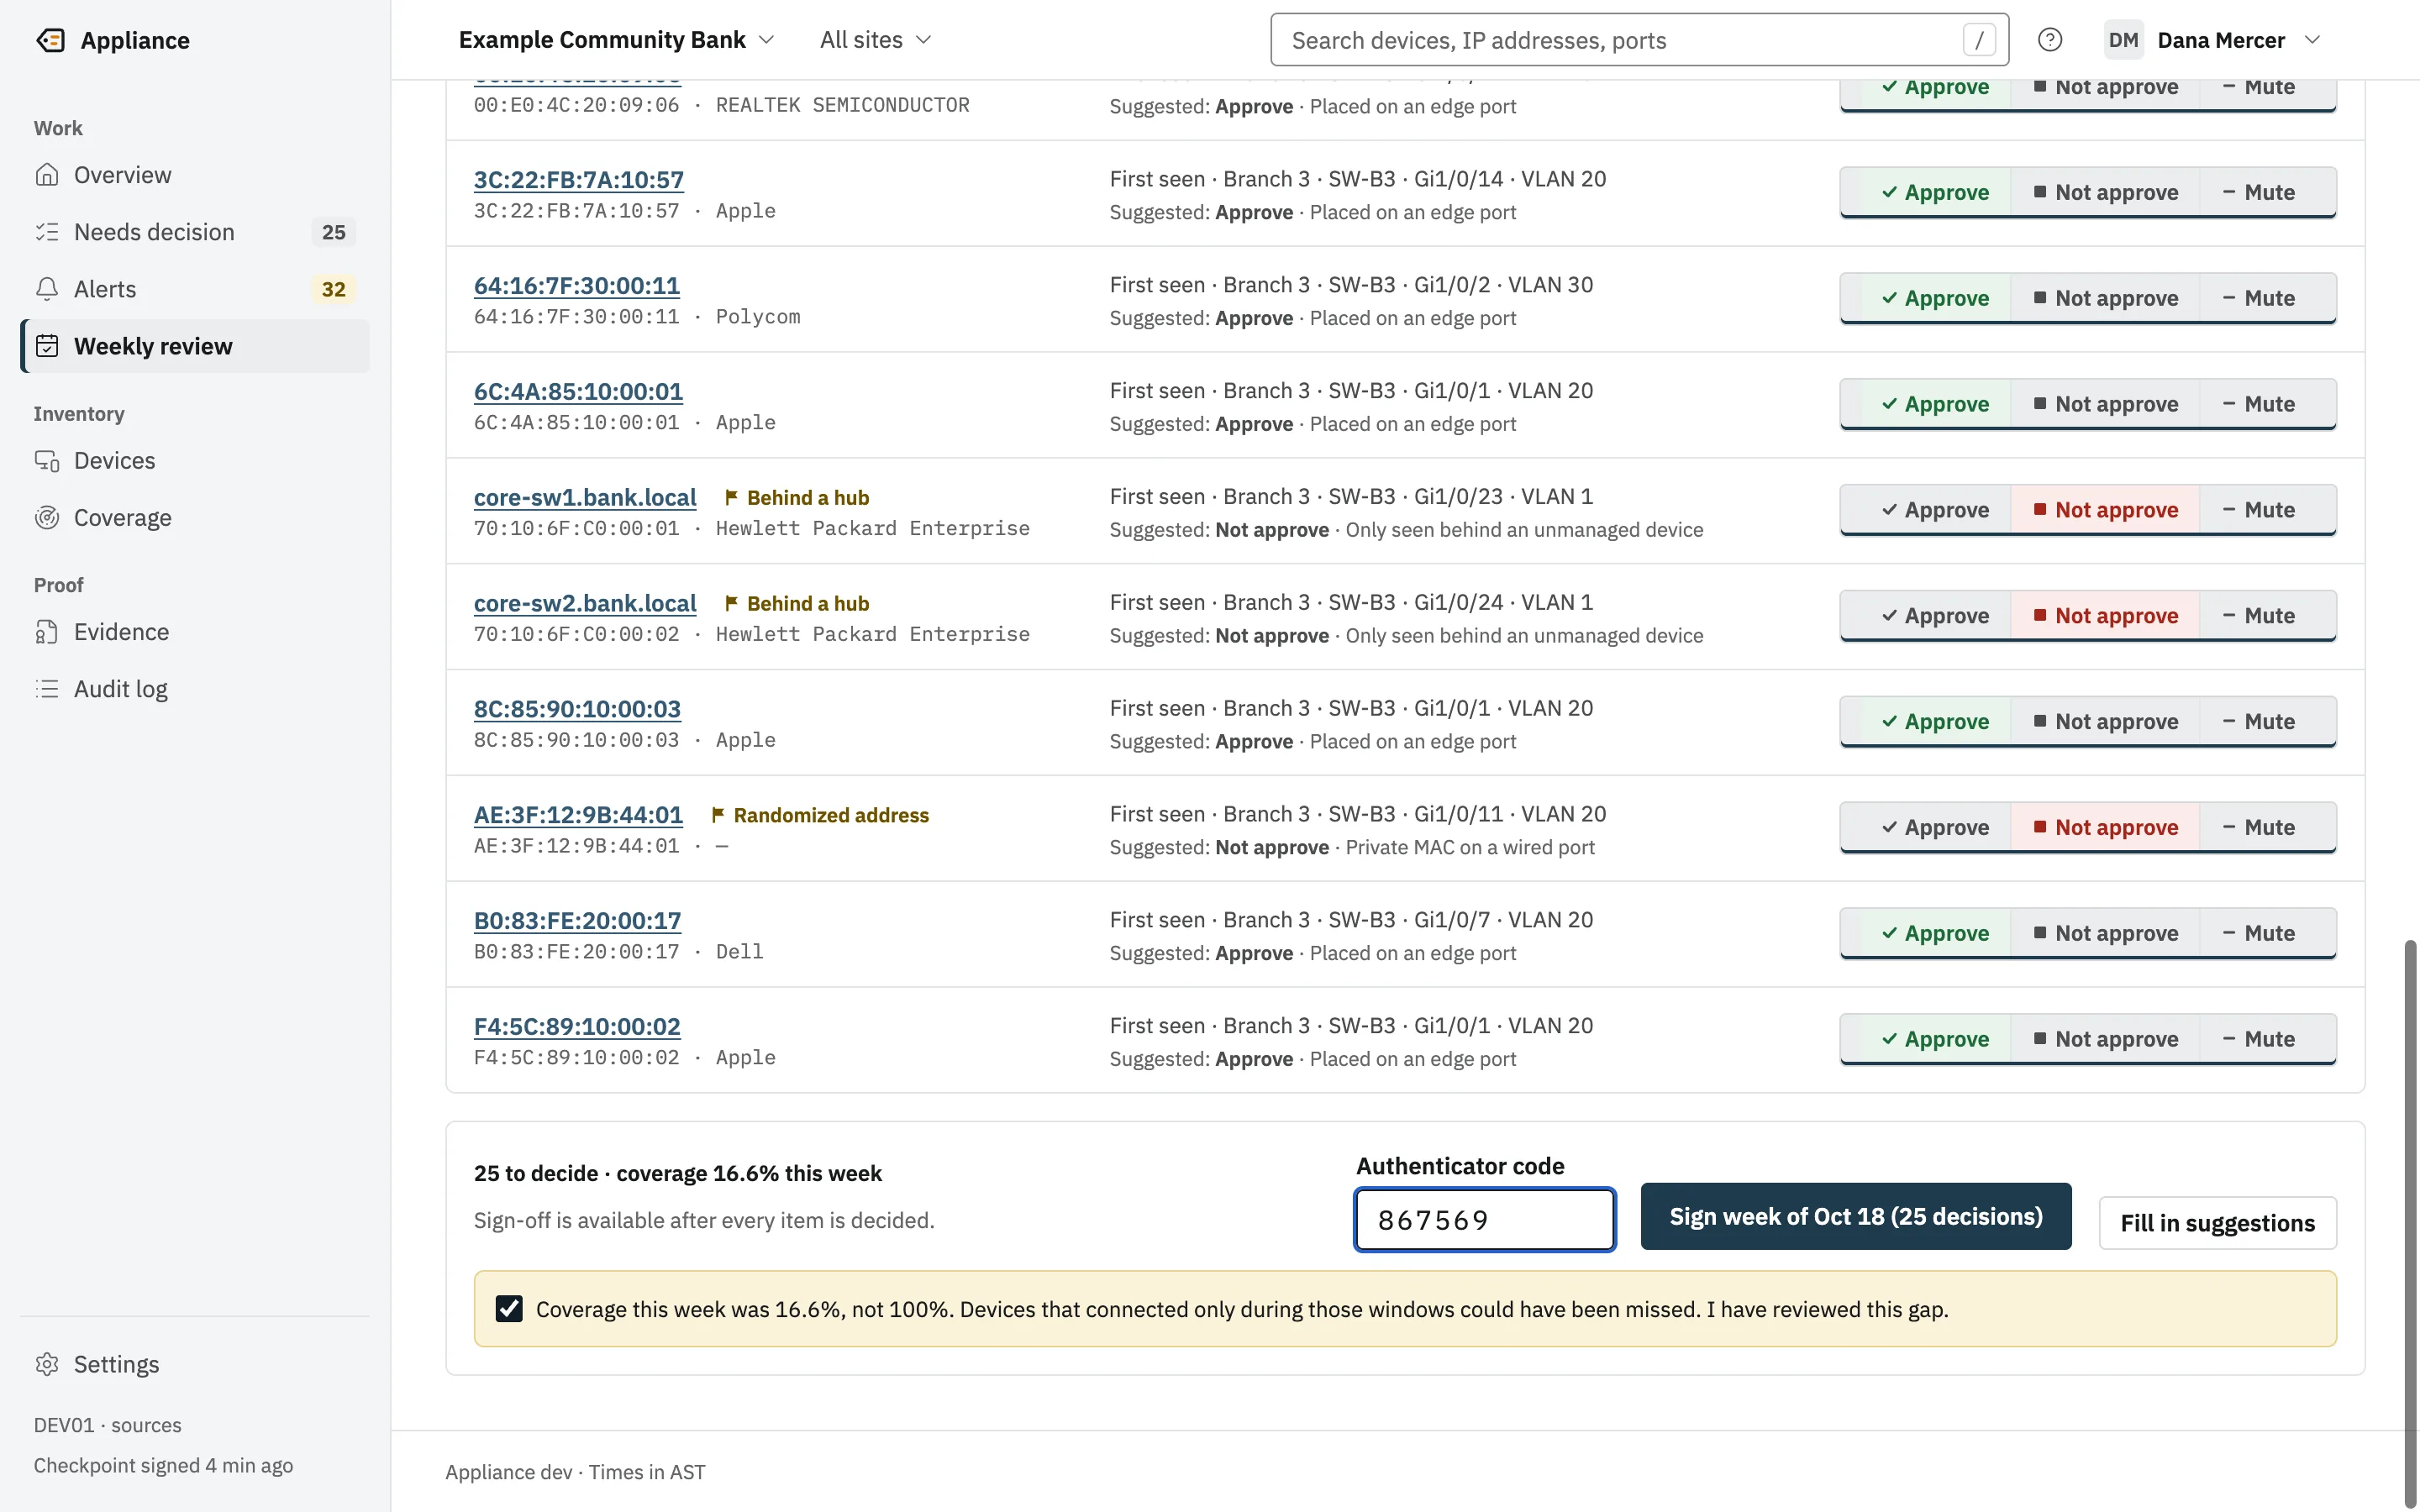
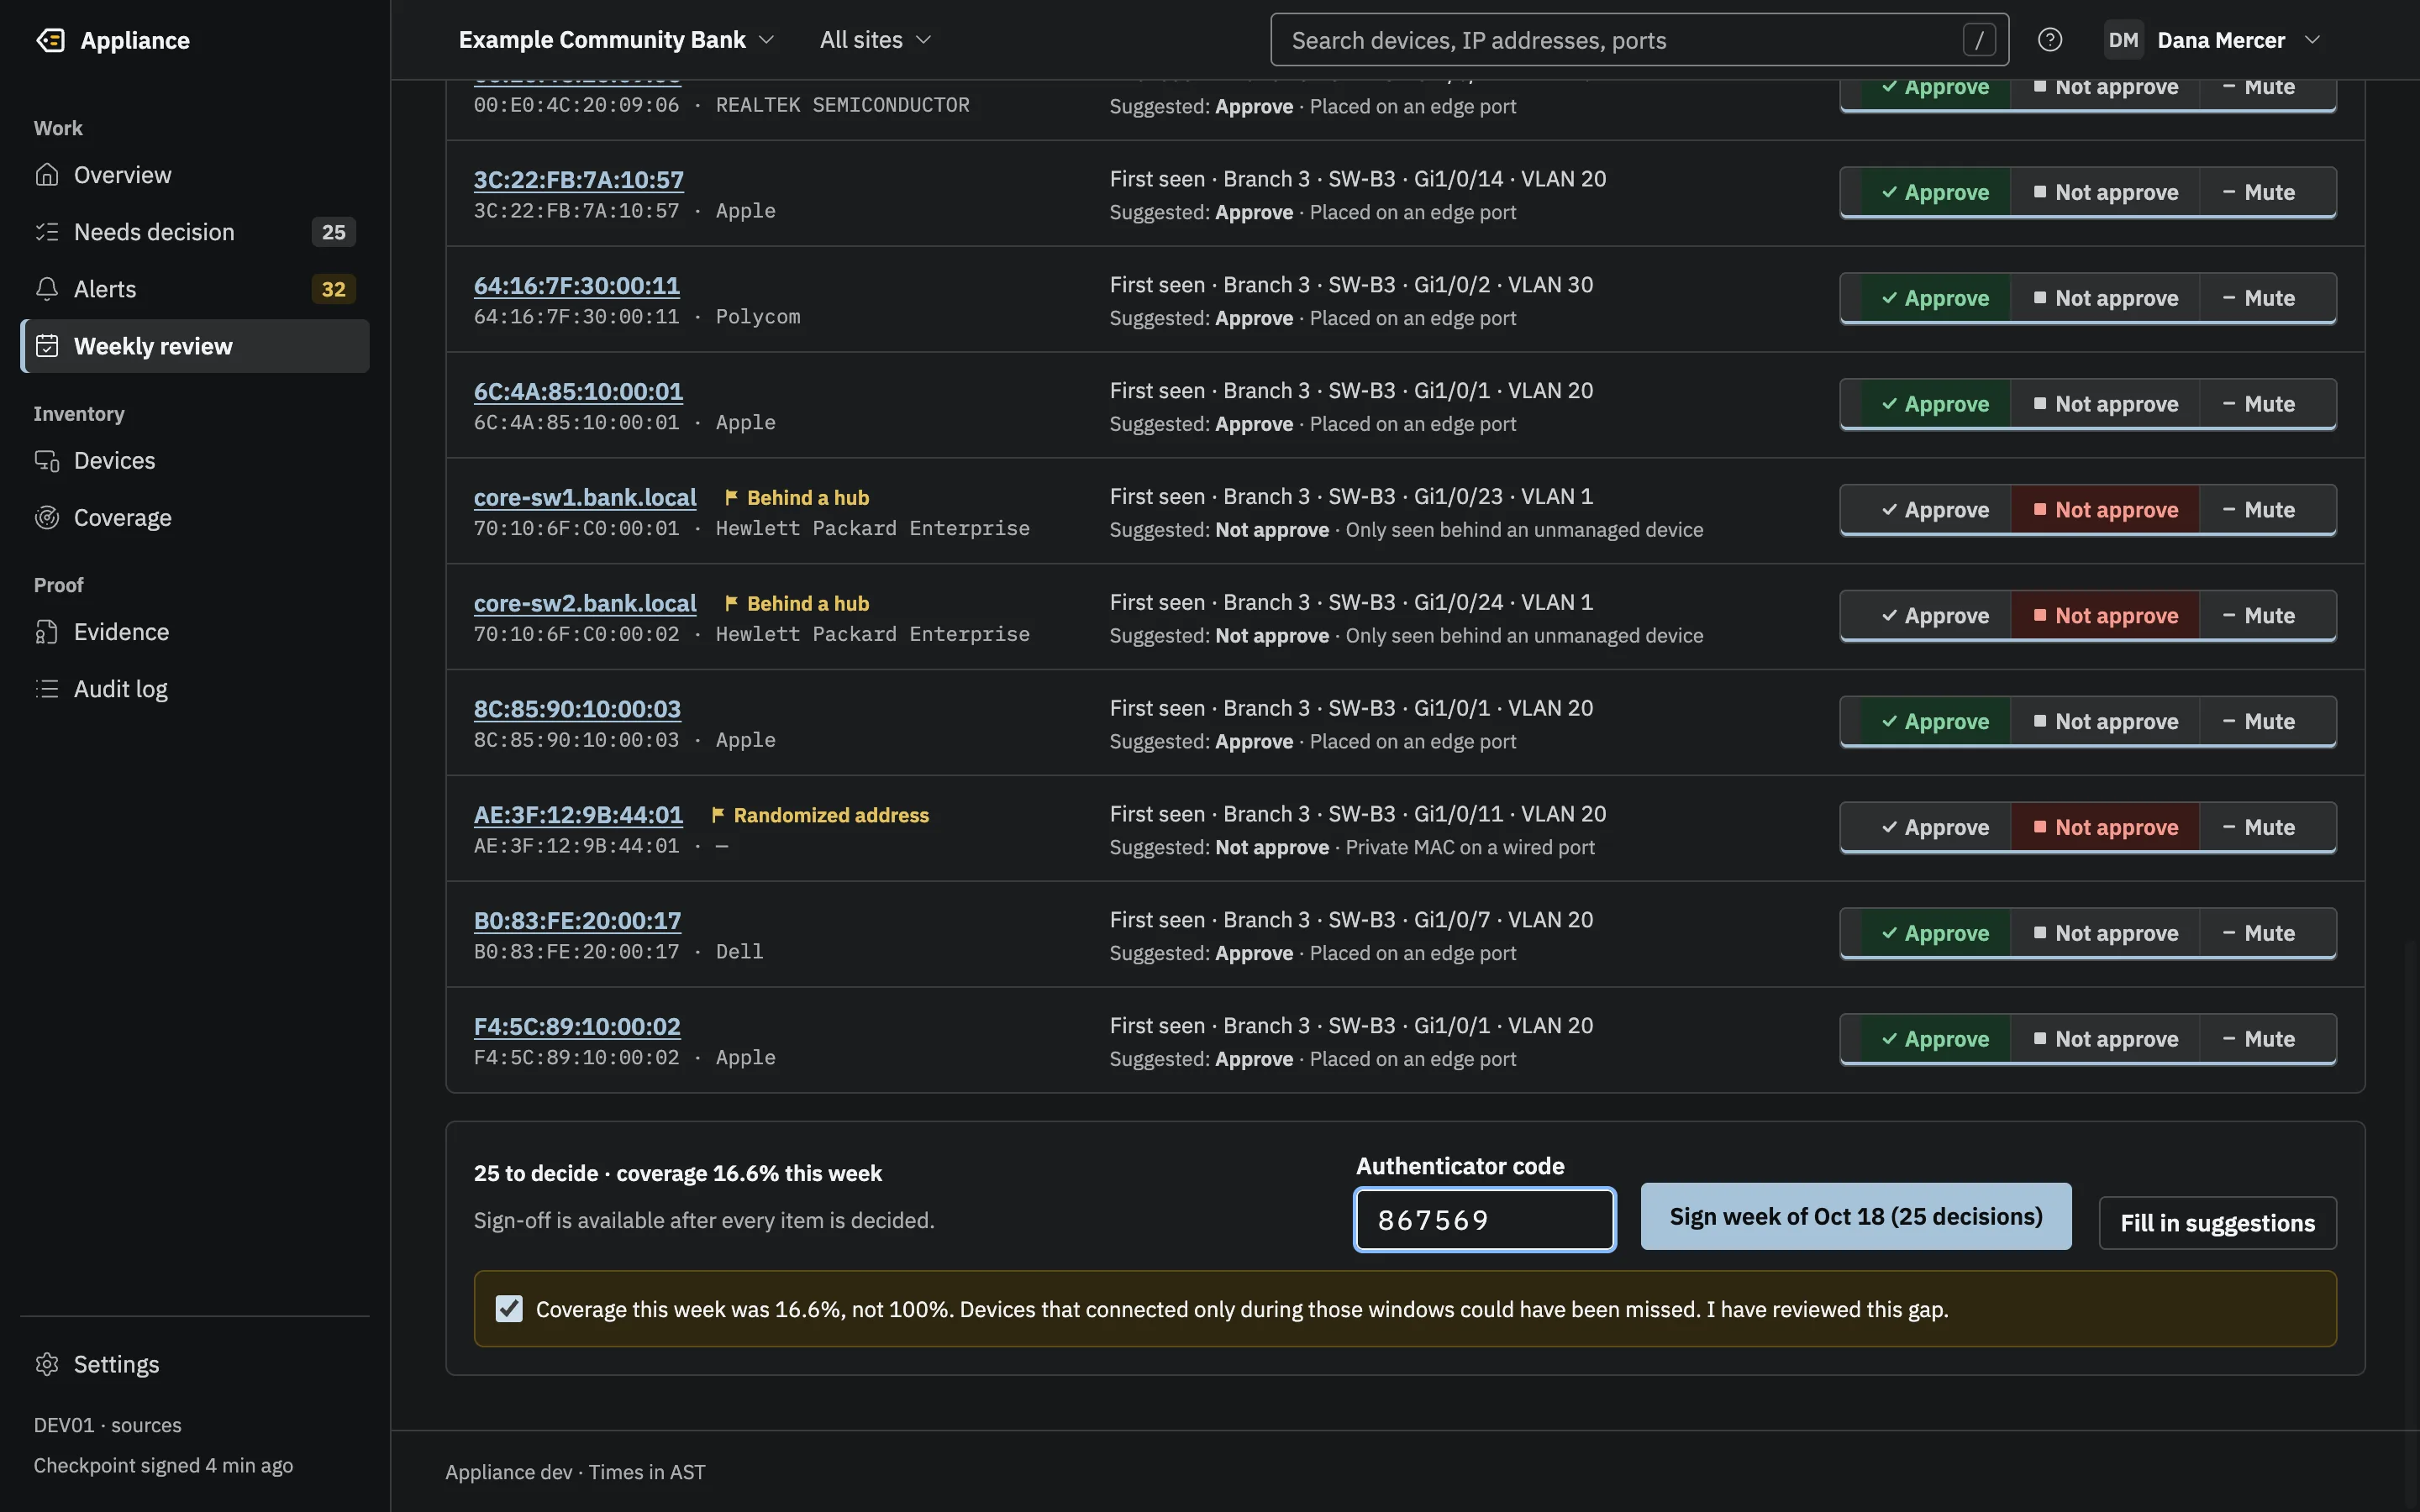
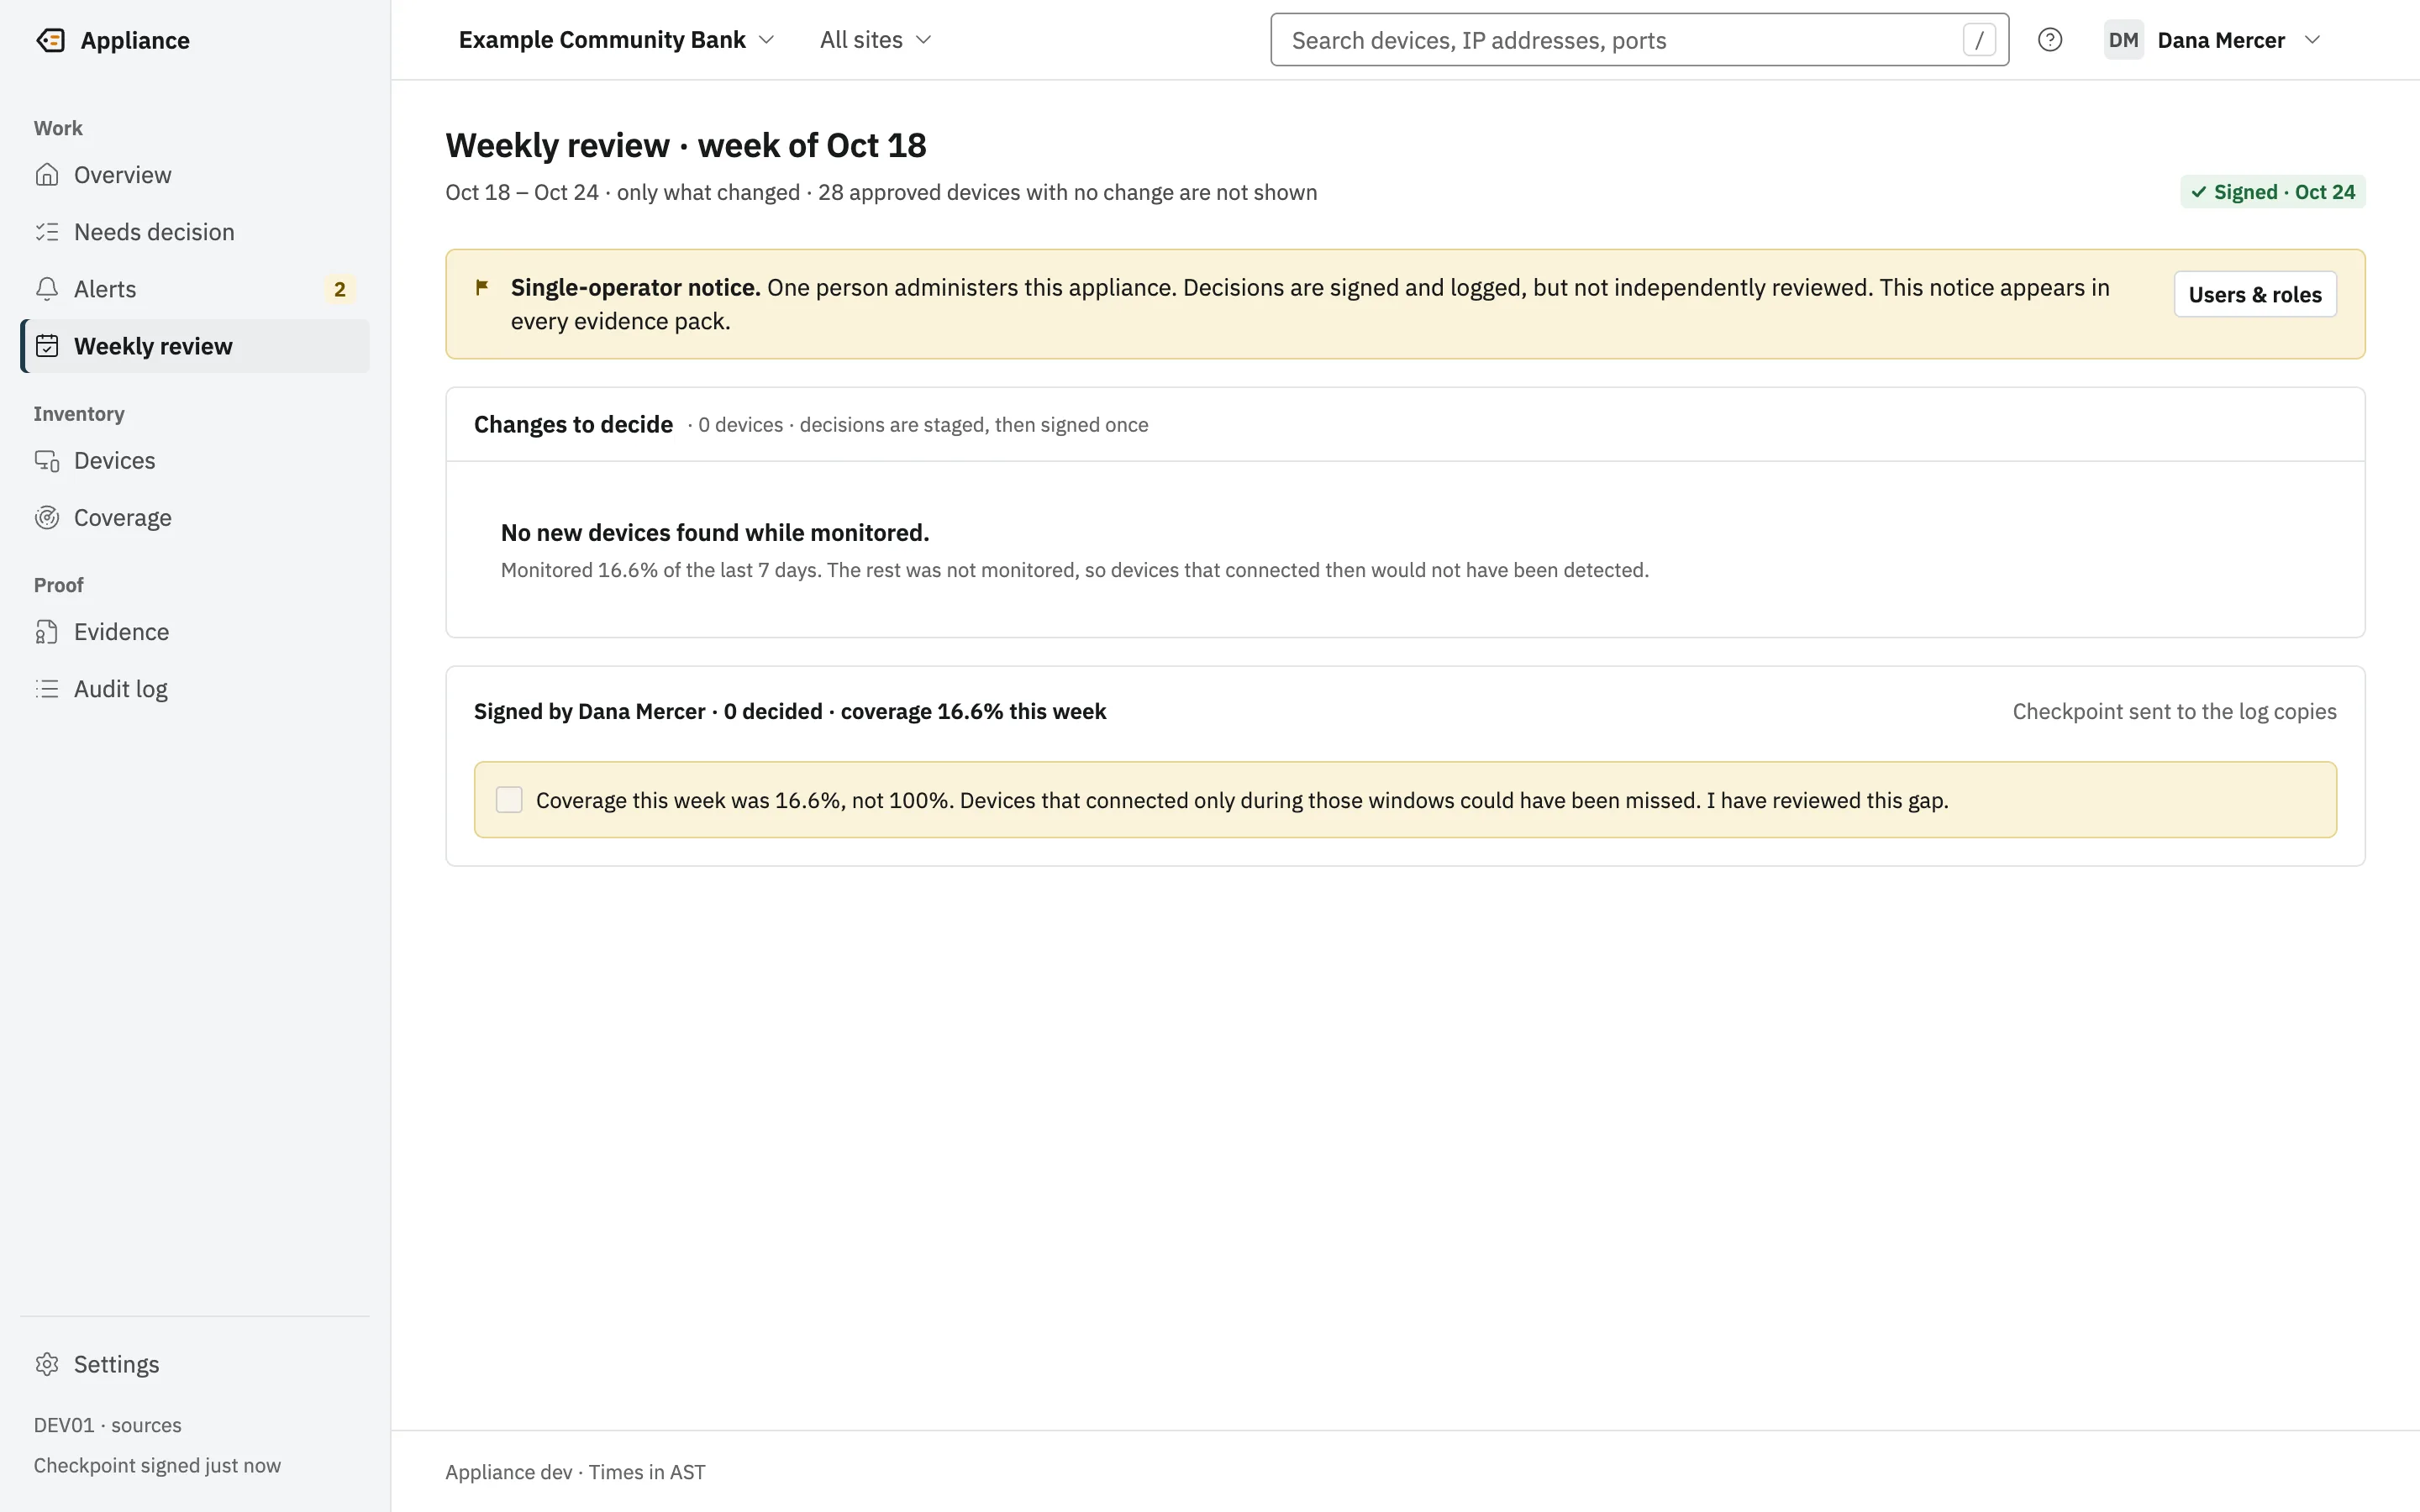
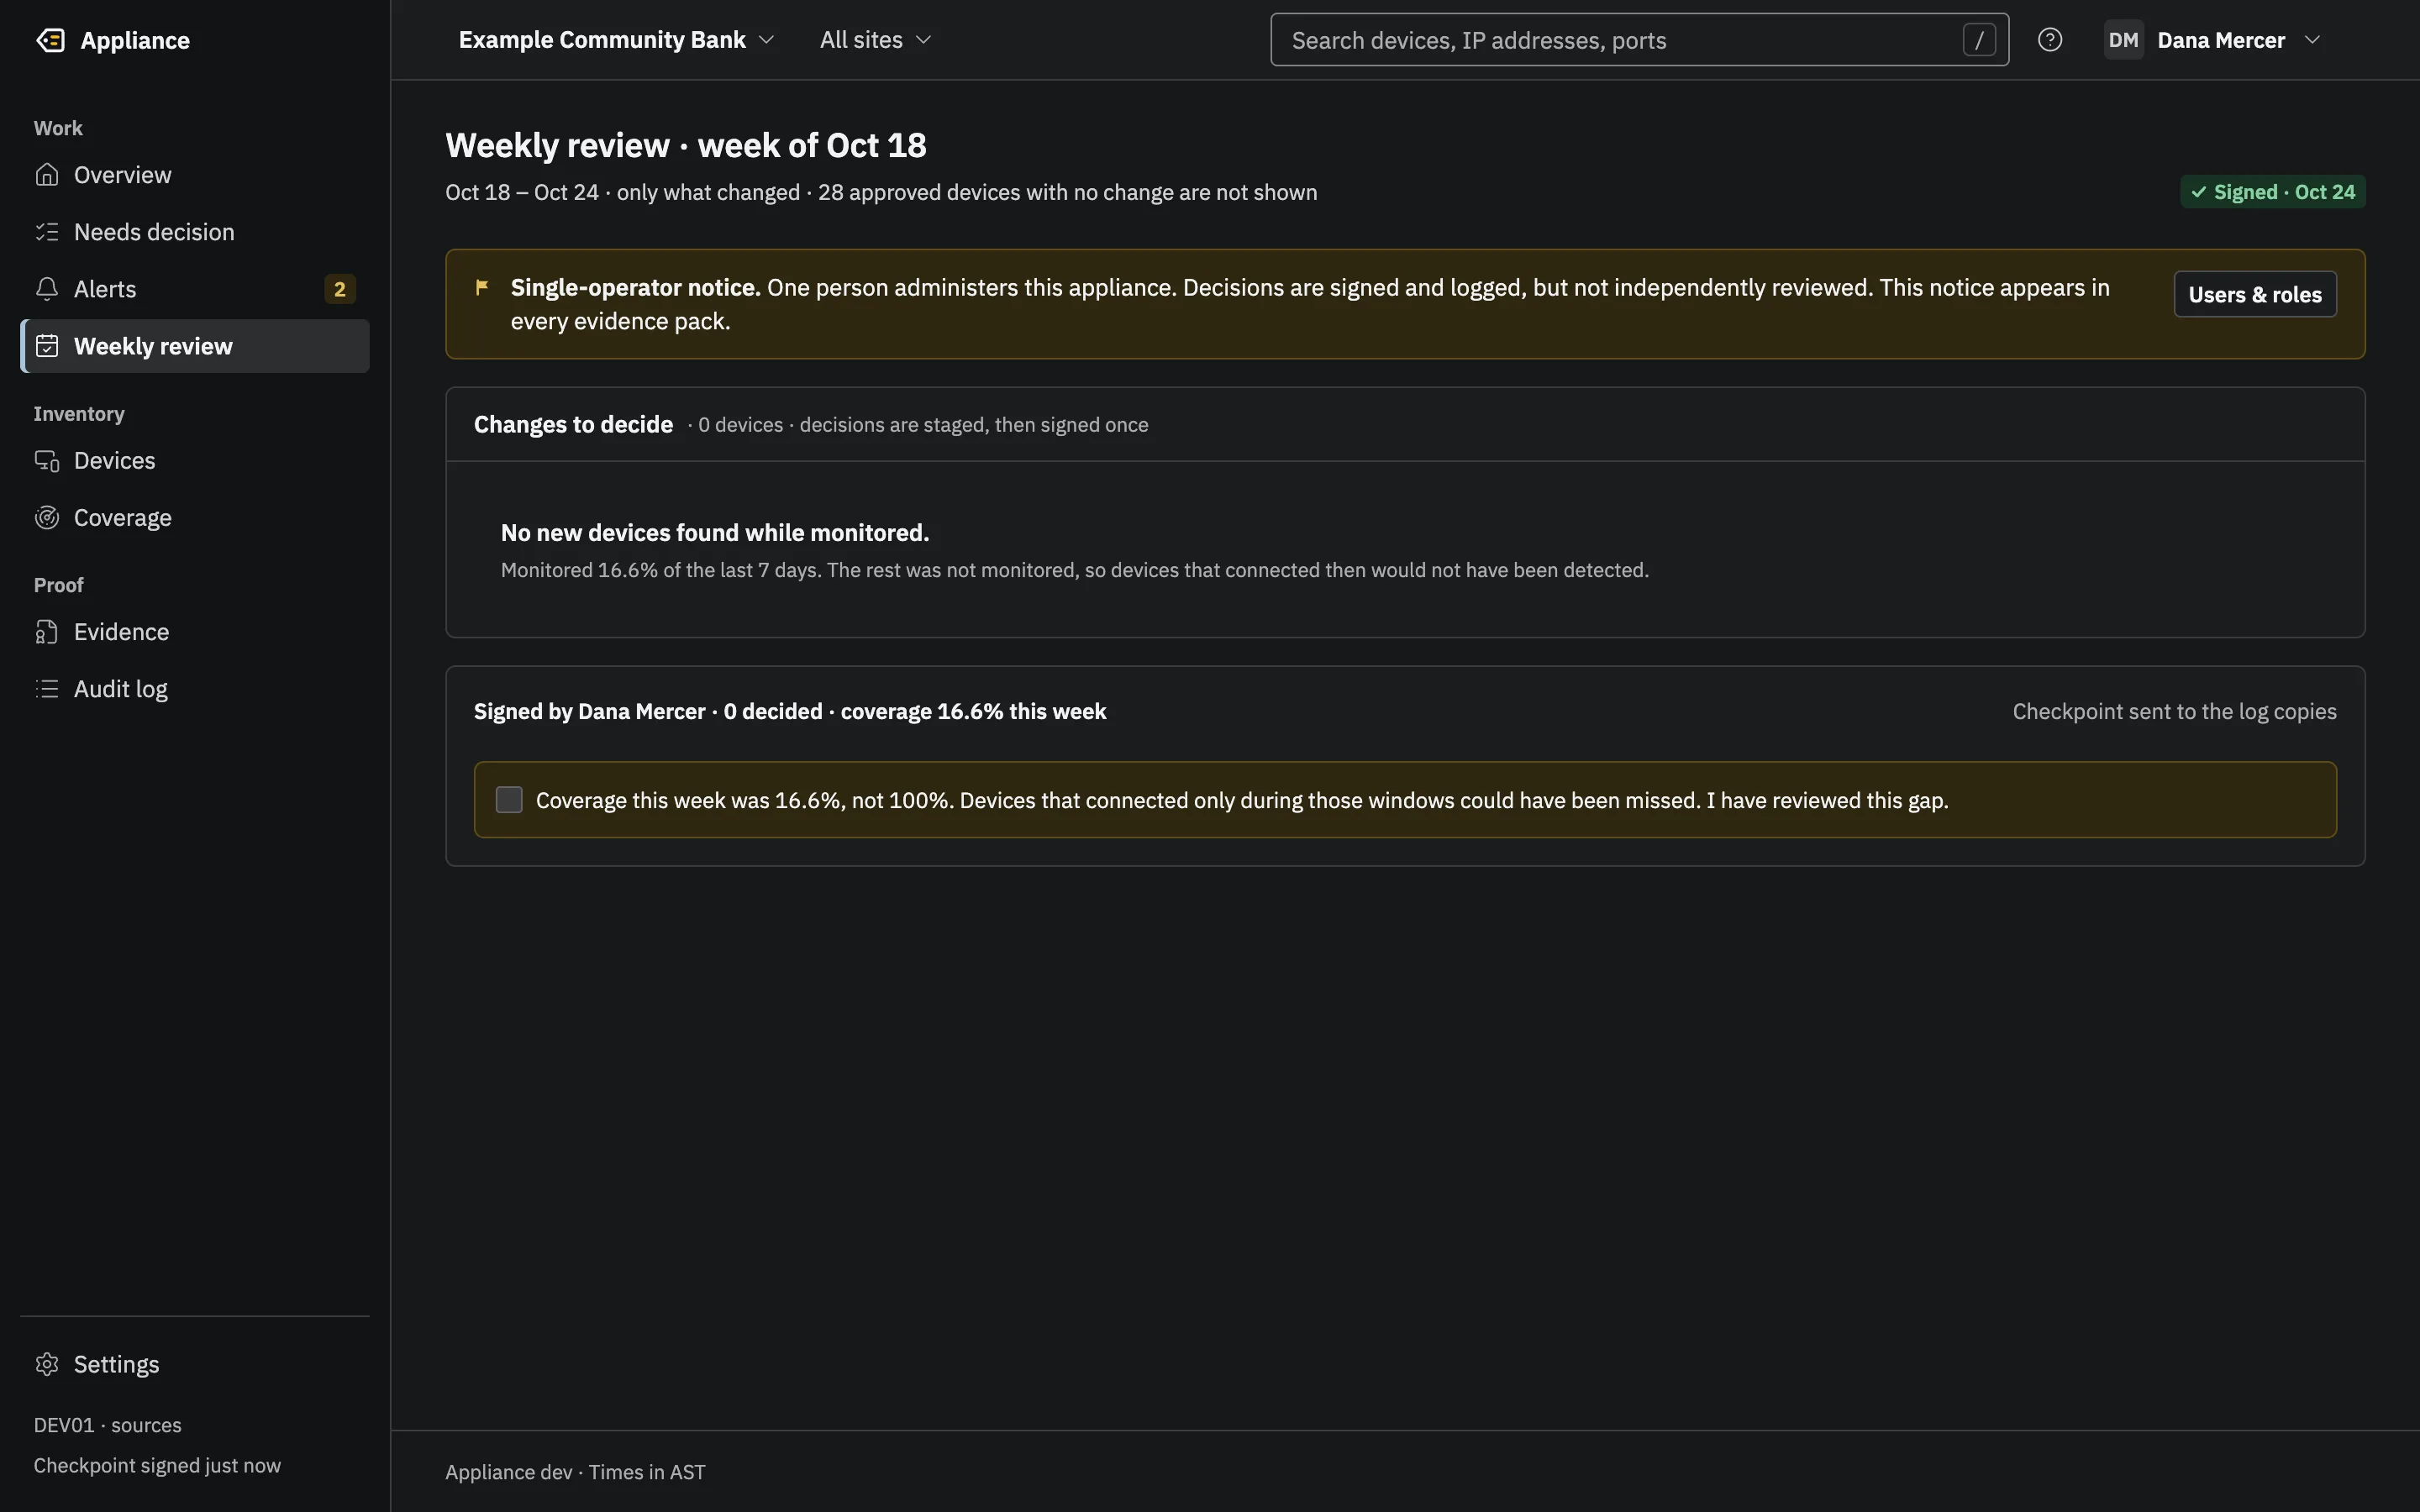
A Reviewer decides every device that changed and signs the week with one code. The sign-off records coverage, who signed and the roles they held.
Examiners expect a periodic, documented review of unauthorized devices, not decisions scattered across months of ad hoc clicks.
The review shows only what changed this week, each with a suggested decision and the reason for it. Choose for each device. Nothing is saved until you sign.
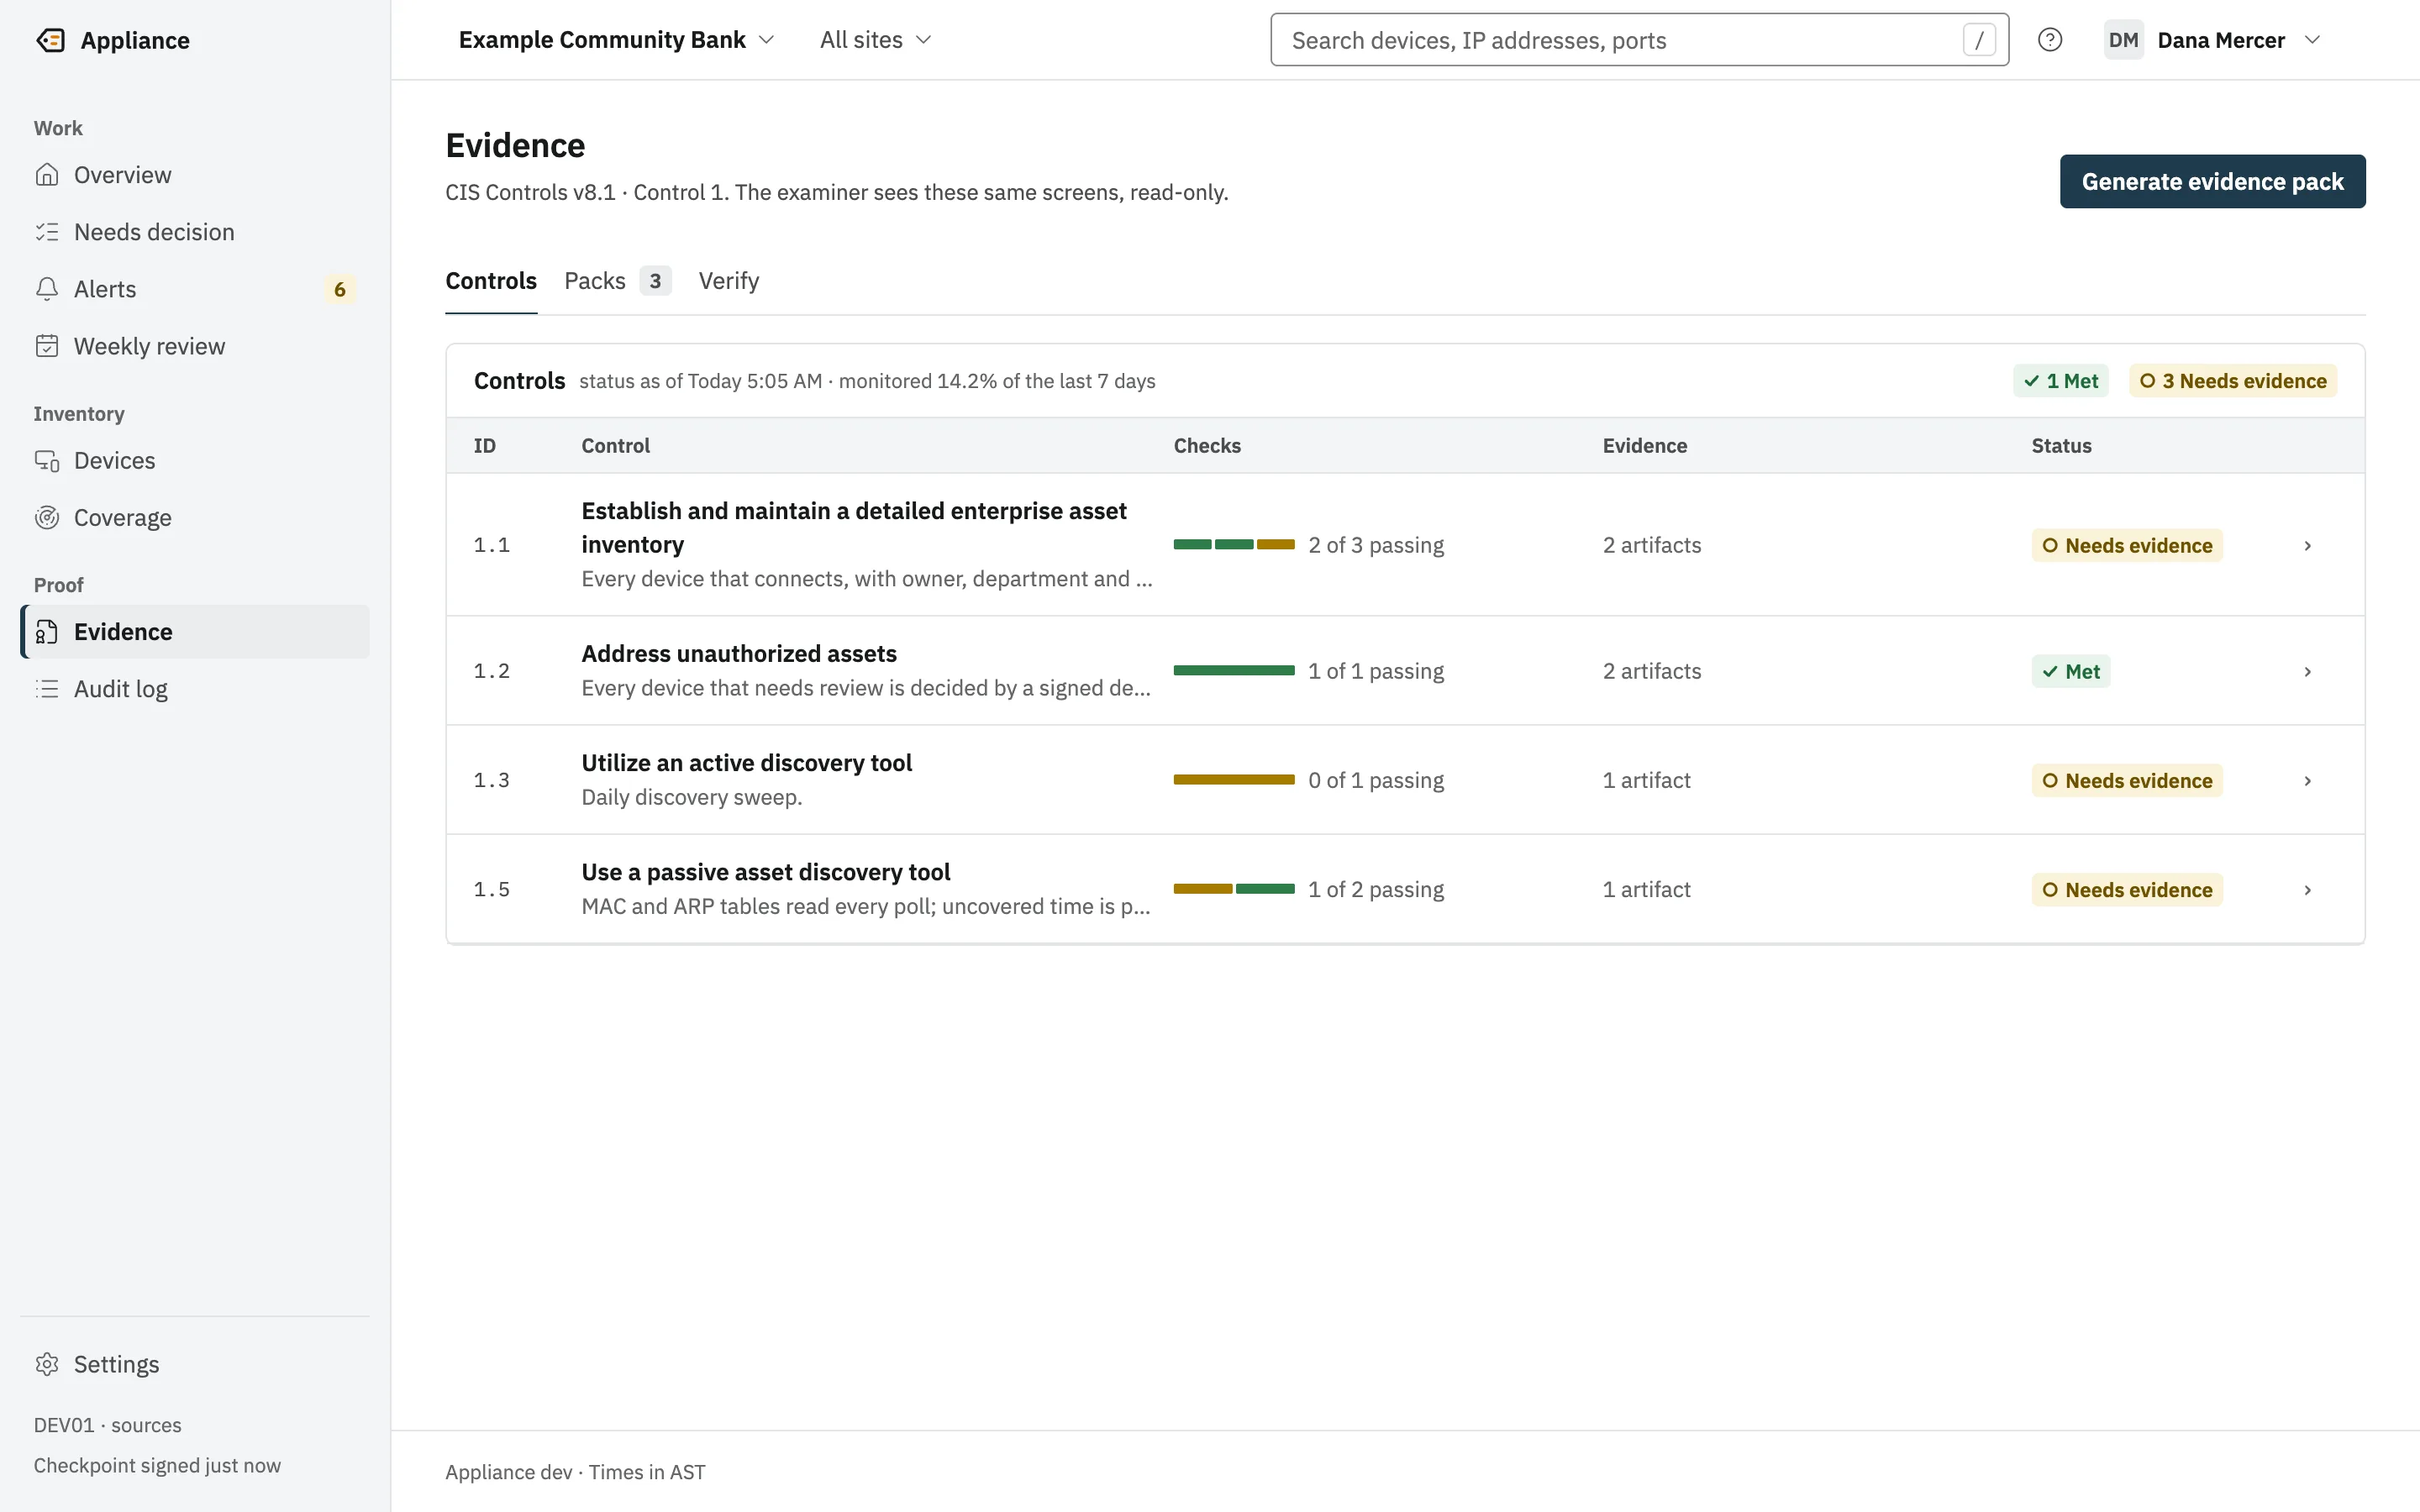
If the appliance was not monitoring the whole week, you acknowledge the gap before you can sign. Signed reviews move the related control to Met only when the evidence is there.
Shown in the new interface, which is in development.
reviews.json in every pack lists each sign-off with the reviewer, how they signed in, their roles, the content hash and the period. The verifier checks each row against its log entry.
Entries this feature writes to the tamper-evident audit log. Each one is in the evidence packs that cover its date.
What it does not do yet, stated plainly. The technical page lists every known gap.
Early access: now taking pilot customers.
A live demo with the engineers who built it. We bring a simulated network; you bring your questions.