Exam preparation usually means screenshots and spreadsheets that the examiner has to take on trust.
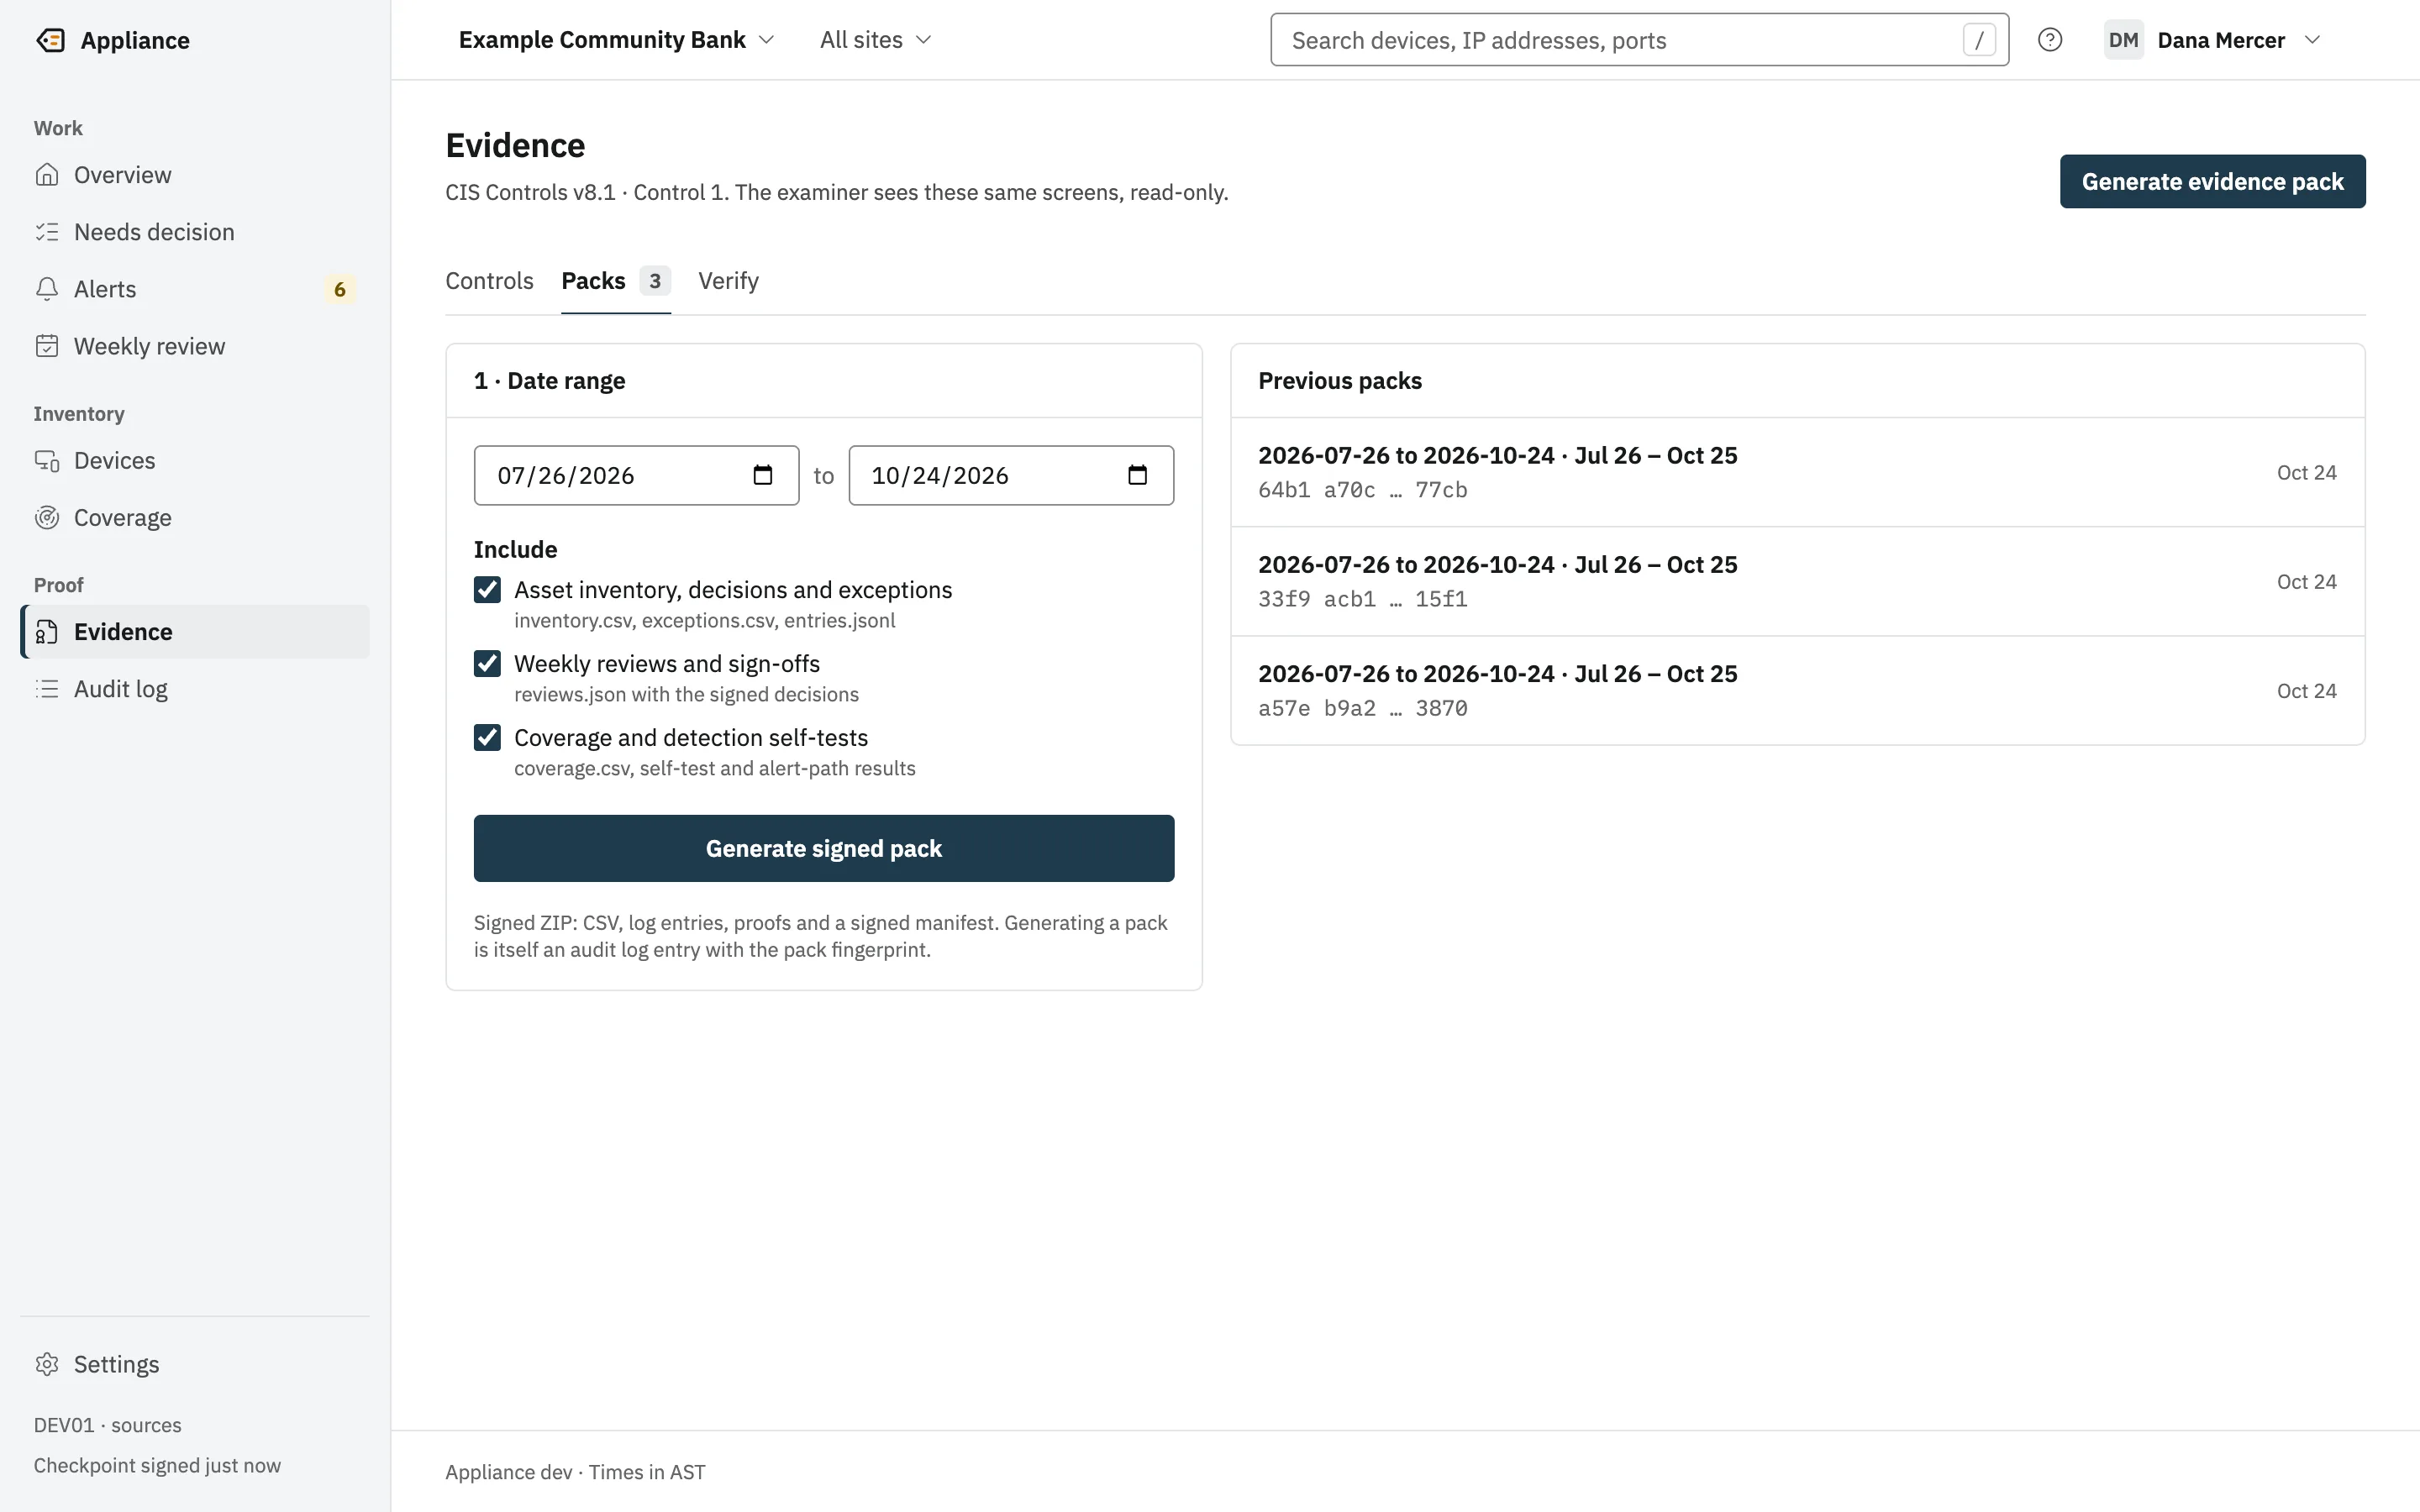
What you see
From switch to examiner. Sources are only read. Every change is a signed log entry. The evidence pack leaves only when you send it, and nothing goes to GigID Labs.What this shows
Inside your network, two switches (SW-HQ-01 and SW-B3) and a firewall (FW-01) are read by the GigID Labs Appliance over SNMPv3, read-only, every 150 seconds; the arrows point into the appliance only. An optional local scan, which a person starts, adds what the attached subnet shows, with no port probes and no credentials. The appliance keeps the device inventory with each device's exact port, the decisions people sign, and a record of where it was and was not looking. Every change becomes an entry in an append-only Merkle log (entries 1,201 to 1,204: a poll, an alert, a decision and a bulk sign-off), and a checkpoint of the log is signed with the appliance's Ed25519 key. An evidence pack, a signed ZIP for any date range, leaves the network only when you send it. The examiner checks it offline on their own computer: registered key, signature, file digests, checkpoint, entries in the log, history and totals, ending in PASS. GigID Labs sits outside your network with no connection to the appliance.
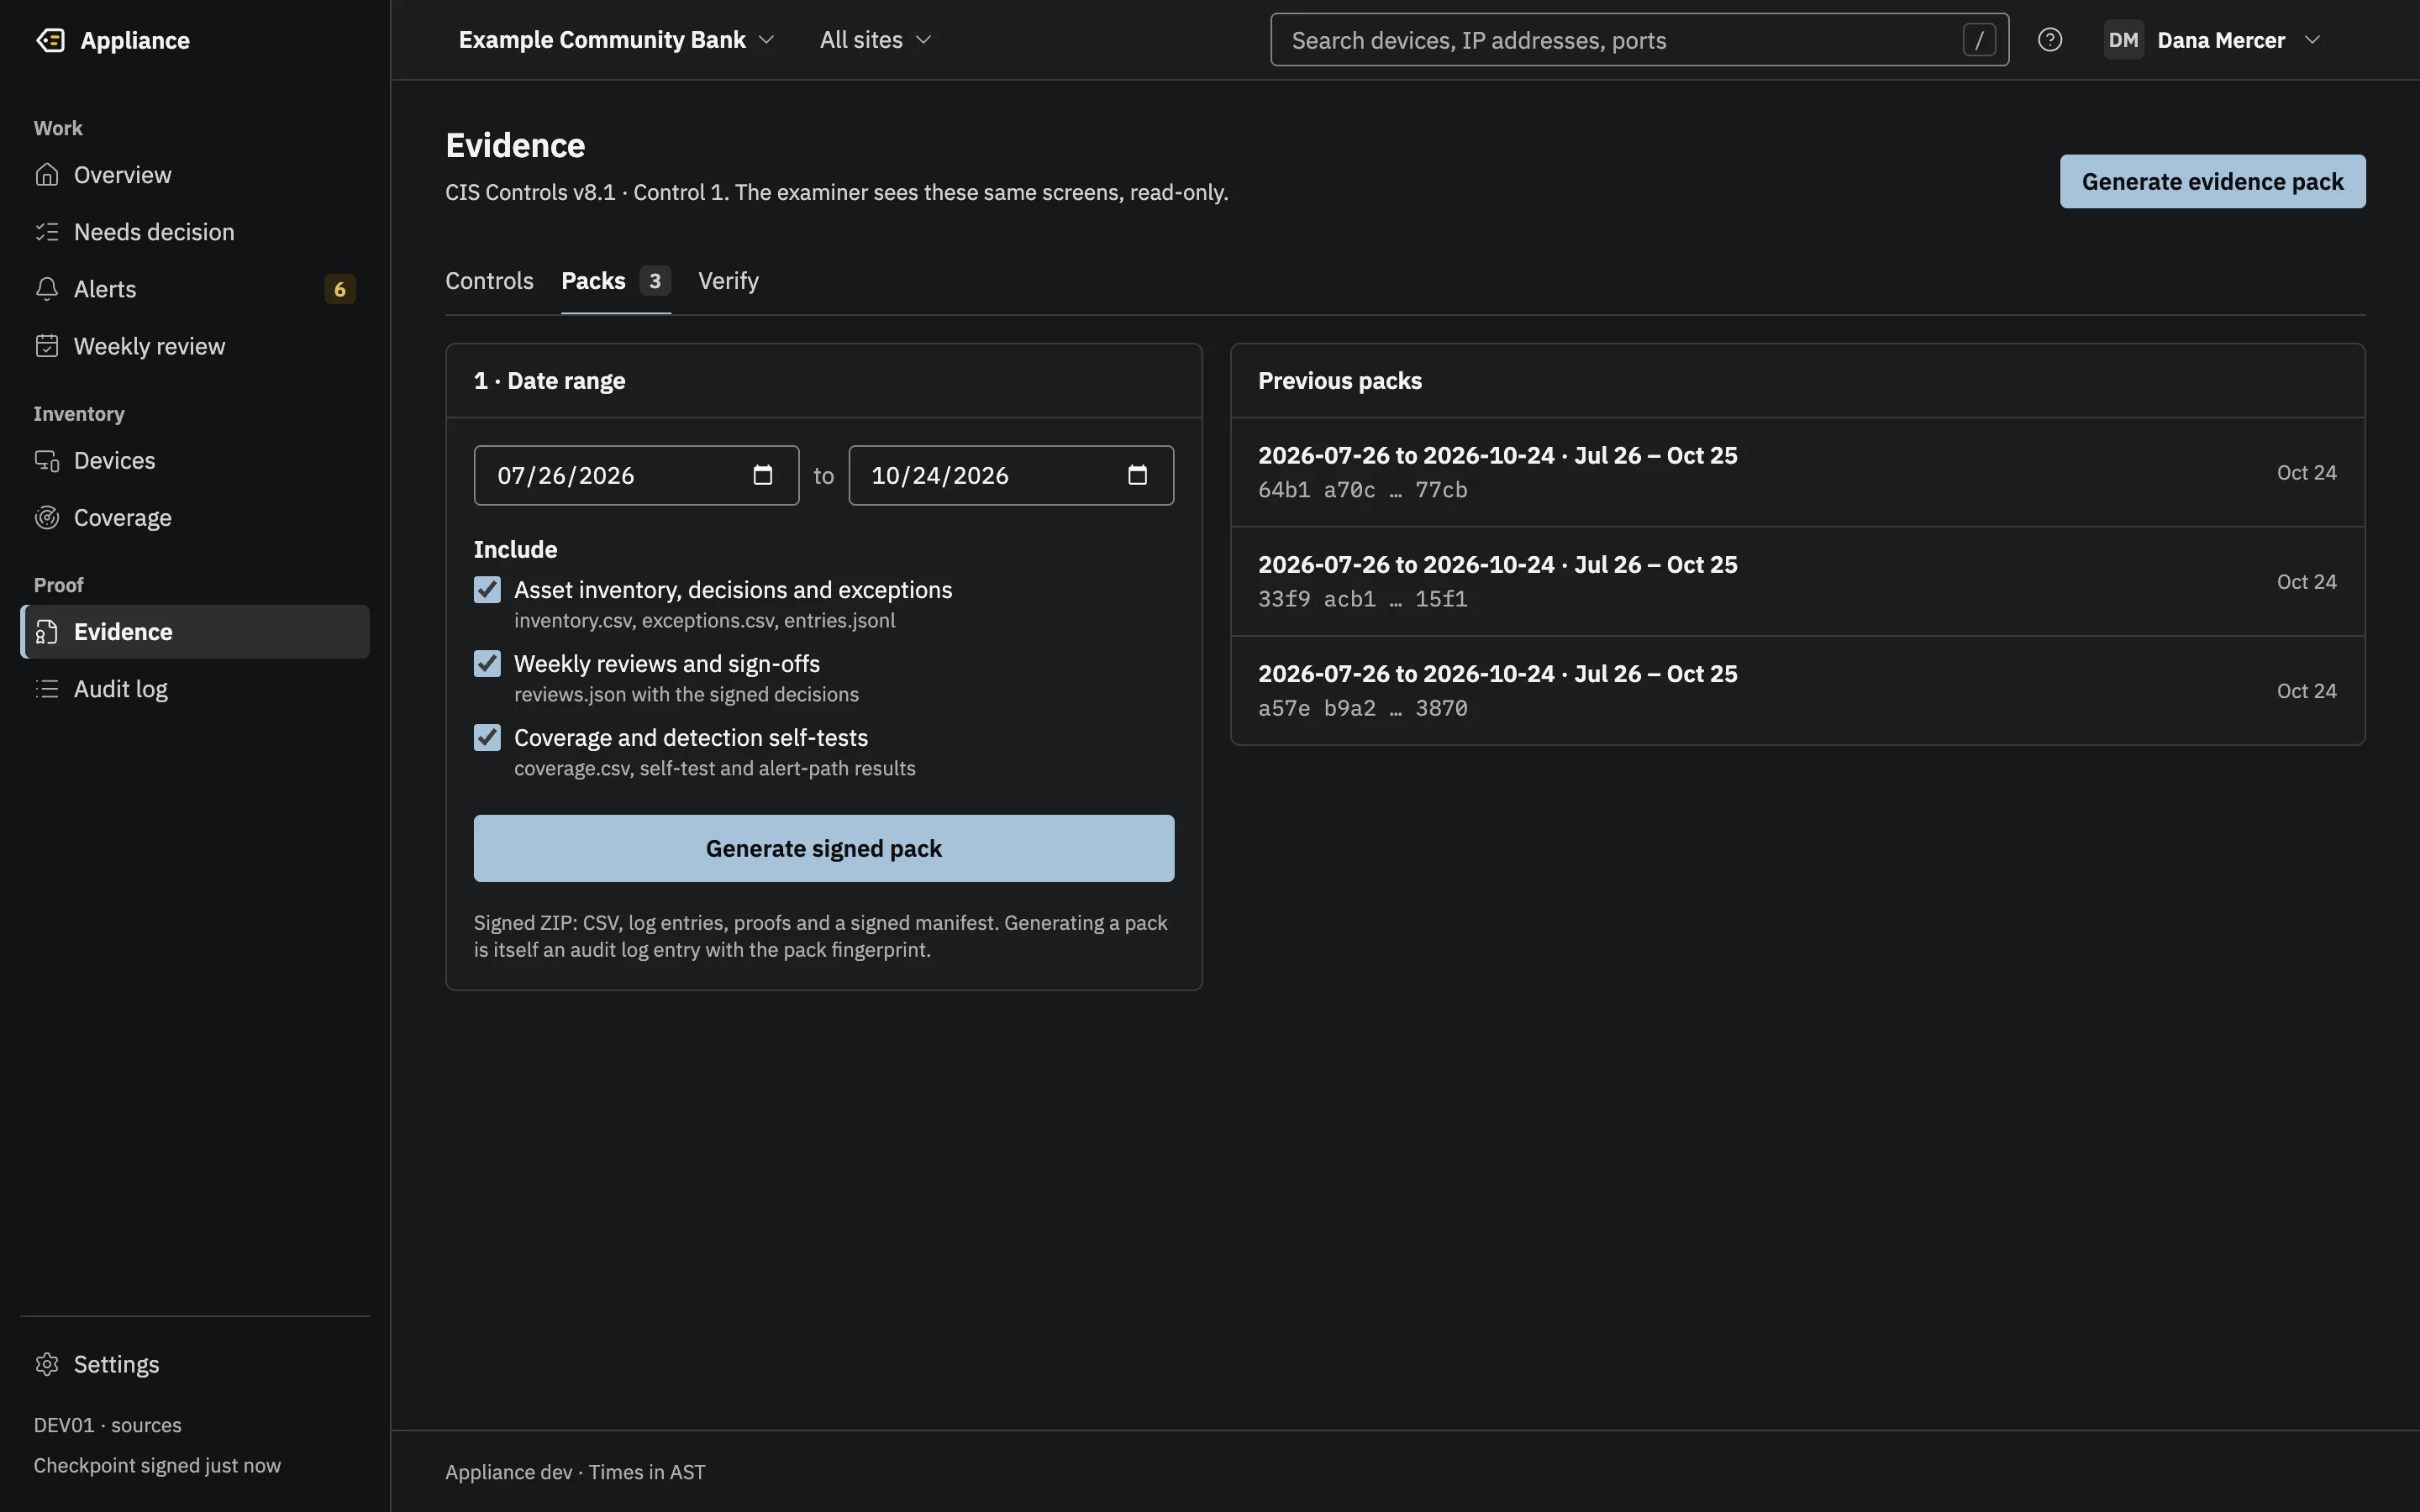
Example CB · EvidenceNew interface, in development
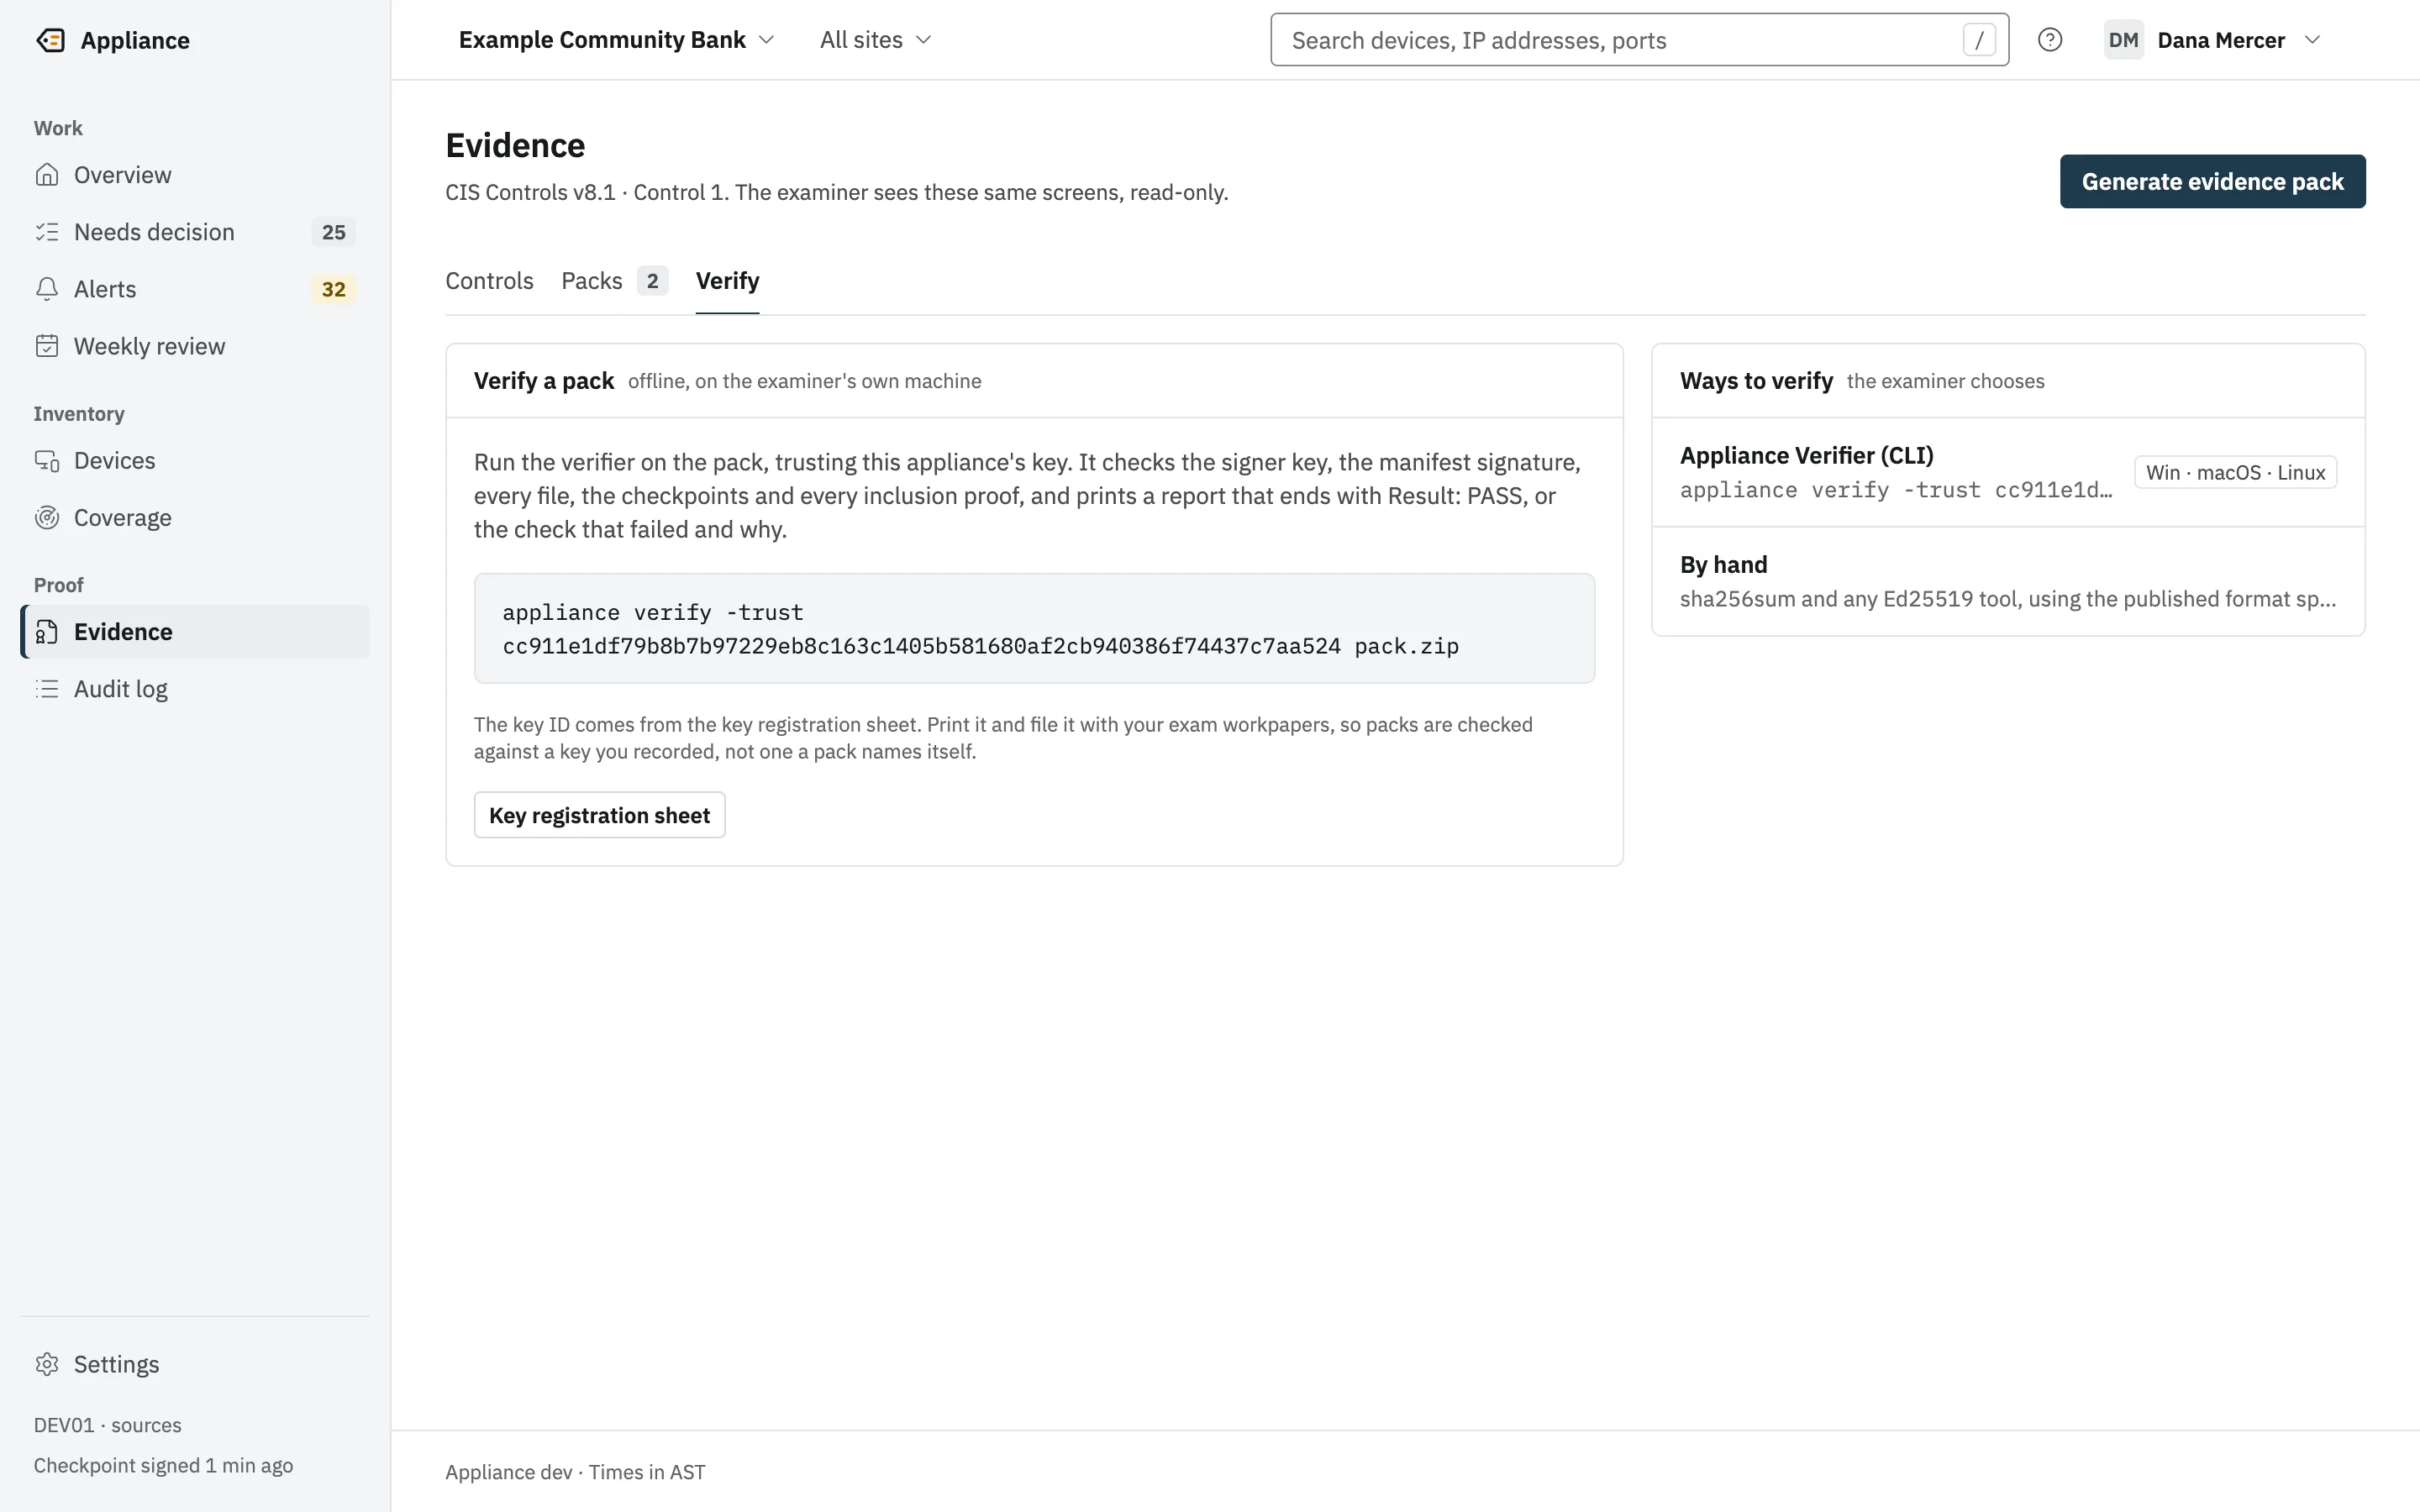
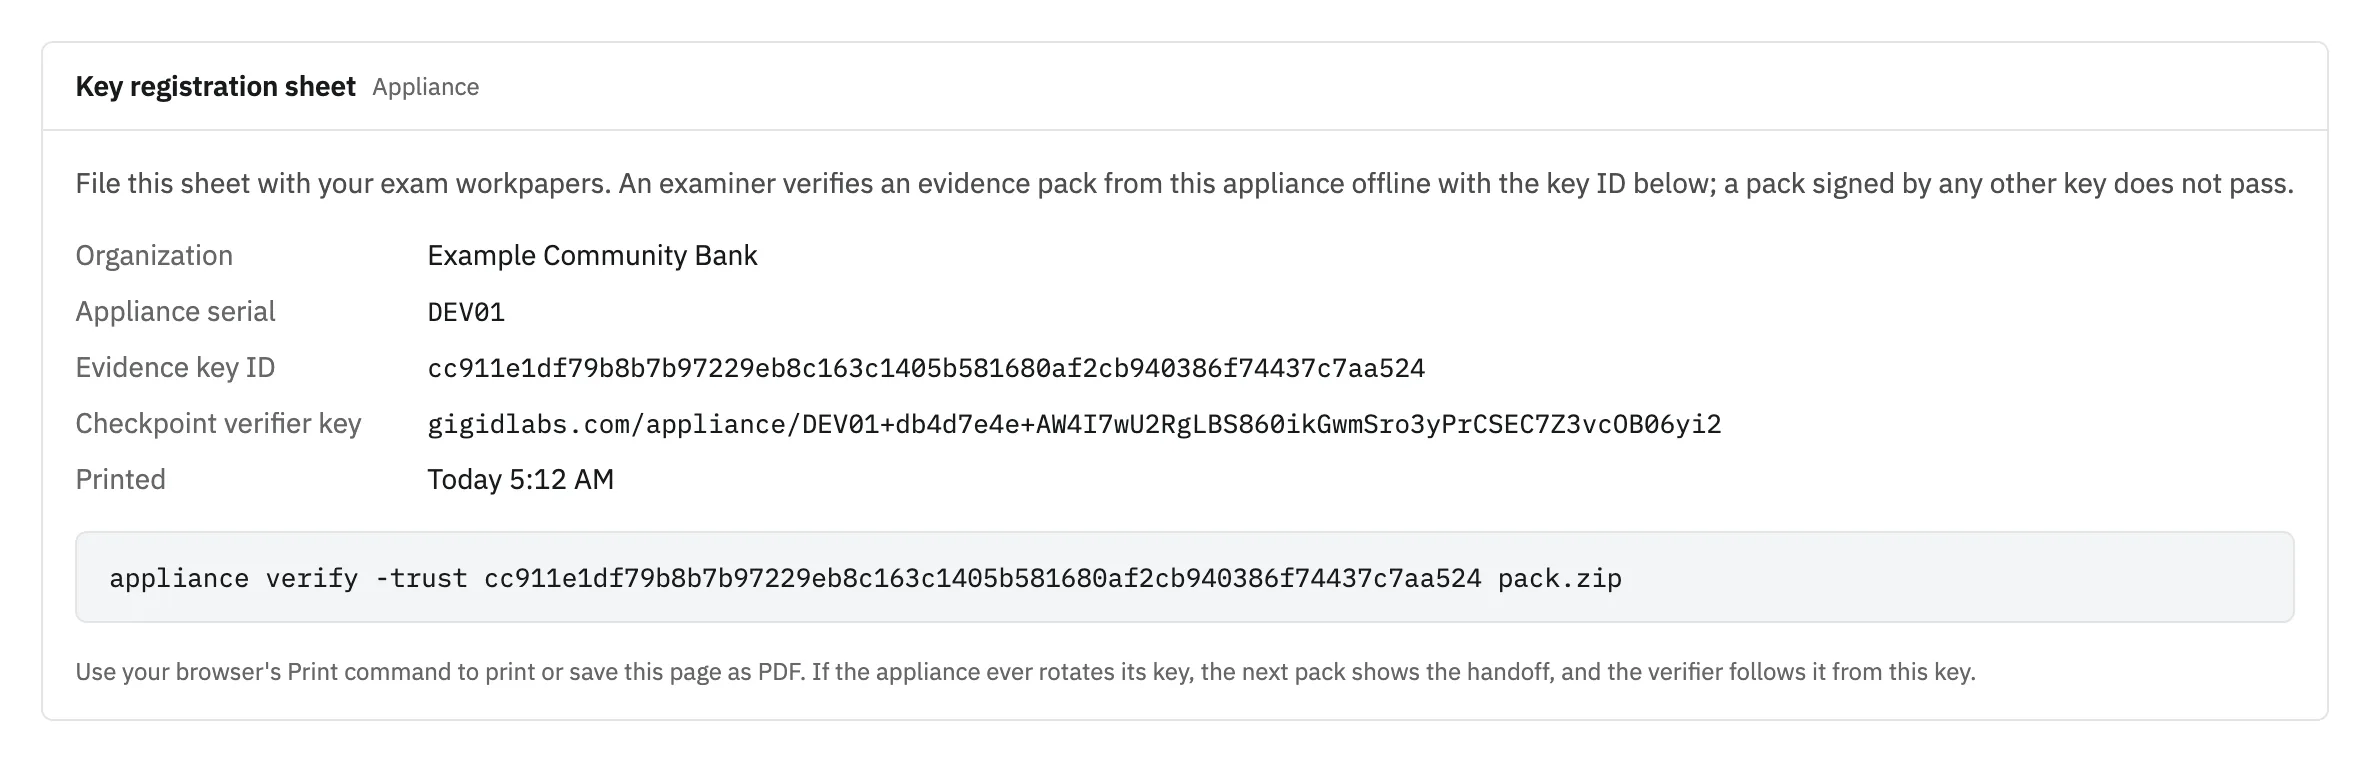
Print the key sheet once and file it with your exam workpapers.
Examiner’s computer: PASS
$ appliance verify -trust cc911e1df79b8b7b97229eb8c163c1405b581680af2cb940386f74437c7aa524 pack.zipEVIDENCE PACK VERIFICATIONResult: PASSVerified at: 2026-10-24T09:05:24ZPack fingerprint: 33f9acb1d1132b67e38b5bd0b2c35123f5b2032a84f8a034be6604fc338815f1Signer key ID: cc911e1df79b8b7b97229eb8c163c1405b581680af2cb940386f74437c7aa524Trusted via: trusted key IDAppliance: DEV01 (version dev)Build digest: 67440c787f3f4a937137e06b54d84cabb5c6ff019e4034733f90e2dd1fd31983Period: 2026-07-26T04:00:00Z to 2026-10-25T04:00:00ZLog: gigidlabs.com/appliance/DEV01, size 181Log root: WQHNjvnRAxCGVYqbAizpIt2v6mD60suPkcokNrjkf0M=Entries: 181 (seq 0 to 180, 2026-10-24T08:50:26Z to 2026-10-24T08:57:52Z)Decisions: 9Reviews: 0Exceptions: 1Devices: approved 8, needs_review 25, not_approved 1Coverage: 100.0% of source-days since install covered (covered 4)Assurance tier: software_protectedDetection proofs: coverageCrosswalk: CIS Controls v8.1 / NIST CSF 2.0 / 12 CFR 30 App. B, 364 App. B, 748 App. A (2026-10)FIPS 140-3 mode: offAnchored to: CHECKPOINTS NOT ANCHOREDSeparation: SINGLE-OPERATOR MODE (one person held Admin and Reviewer)History: NOT CHECKED against an independent checkpointChecks: 1. Signing key is trusted (registration sheet or previous pack) PASS key cc911e1df79b8b7b97229eb8c163c1405b581680af2cb940386f74437c7aa524, trusted via trusted key ID 2. Manifest signature (DSSE, Ed25519) is valid PASS Ed25519 signature over the manifest is valid 3. Every file matches its SHA-256 in the manifest PASS 18 files match their manifest digests 4. Checkpoint signature is valid and matches the manifest PASS checkpoint for gigidlabs.com/appliance/DEV01 at size 181 is signed by a trusted key 5. Every entry has a valid inclusion proof to the checkpoint PASS 181 entries (seq 0 to 180) and 9 cited entries are in the signed log 6. History is consistent with earlier checkpoints NOT_CHECKEDNOT CHECKED: no independent checkpoint (previous pack, SIEM or email) was supplied; the pack's own consistency proofs from 1 earlier pack checkpoint(s) are valid 7. Recomputed totals match the manifest counts PASS entries, decisions, reviews, exceptions, devices and coverage all match[exit 0]
Real output: PASS on a pack from the test appliance, with its disclosures printed, not hidden.
Examiner’s computer: TAMPERED
$ appliance verify -trust cc911e1df79b8b7b97229eb8c163c1405b581680af2cb940386f74437c7aa524 pack-edited.zipEVIDENCE PACK VERIFICATIONResult: TAMPEREDReason: inventory.csv has SHA-256 00951cdee49cd0043f6c0b330b264e169f5145a4427582bbd913781b10a6e2b0, manifest says d1a167f91c009a0ede446cb27fd4b7f46653c20f11327be06d0949fdefa65532Verified at: 2026-10-24T09:05:24ZPack fingerprint: 33f9acb1d1132b67e38b5bd0b2c35123f5b2032a84f8a034be6604fc338815f1Signer key ID: cc911e1df79b8b7b97229eb8c163c1405b581680af2cb940386f74437c7aa524Trusted via: trusted key IDChecks: 1. Signing key is trusted (registration sheet or previous pack) PASS key cc911e1df79b8b7b97229eb8c163c1405b581680af2cb940386f74437c7aa524, trusted via trusted key ID 2. Manifest signature (DSSE, Ed25519) is valid PASS Ed25519 signature over the manifest is valid 3. Every file matches its SHA-256 in the manifest FAIL inventory.csv has SHA-256 00951cdee49cd0043f6c0b330b264e169f5145a4427582bbd913781b10a6e2b0, manifest says d1a167f91c009a0ede446cb27fd4b7f46653c20f11327be06d0949fdefa65532 4. Checkpoint signature is valid and matches the manifest SKIPPED 5. Every entry has a valid inclusion proof to the checkpoint SKIPPED 6. History is consistent with earlier checkpoints SKIPPED 7. Recomputed totals match the manifest counts SKIPPED[exit 4]
The same pack with one row of inventory.csv changed: TAMPERED, naming the file.
How it works
Inside: a signed manifest listing every file and its SHA-256, the signed checkpoint, every log entry in the range, the proofs that tie them to the checkpoint, and inventory, exceptions, coverage and review files.
The manifest is an in-toto statement in a DSSE envelope, signed with Ed25519. Every JSON file is canonical, so one value has exactly one encoding.
The examiner runs seven checks: the signing key, the signature, every file’s hash, the checkpoint, every entry’s inclusion proof, history against earlier packs, and the totals. One verdict, no network needed.
Trust comes from one value the examiner holds separately: the key ID on the printed key registration sheet.
The verifier fails closed. A pack that was unzipped and zipped again is refused.
Before writing a pack, the appliance re-checks every entry against the signed checkpoint, so a problem shows at export, not in front of an examiner.
What it proves
The examiner gets the raw evidence and cryptographic proof that it is complete for the period and unchanged since signing. They can check both without trusting the bank’s administrator or GigID Labs.
What it records
Entries this feature writes to the tamper-evident audit log. Each one is in the evidence packs that cover its date.
pack_exportedThe pack’s fingerprint. Later packs prove consistency from it.
key_registeredThe evidence key the packs are signed with.
Limits
What it does not do yet, stated plainly. The technical page lists every known gap.
There is no PDF version of a pack yet.
Newer record types, such as tripwire trips and reconcile imports, are in the entries files but do not have their own summary files yet.
The verifier is the verify mode of the same program, plus a published by-hand procedure. A separate public download is not available yet.
Every sign-in, decision and change is an entry in an append-only Merkle log with signed checkpoints, and polling is recorded as hourly roll-ups plus every change in a poll’s result. Editing an old entry breaks every checkpoint after it.